GHSA-hvp5-5x4f-33fq: JADX file override vulnerability
Noroxi assessment
Priority: Monitor (action score 13/100)
- The sources we track (CISA KEV, Exploit-DB, Metasploit, Nuclei, GitHub) show no public exploit code or exploitation in the wild.
- Someone with local access to the system can trigger it. A low-privileged account is enough. No user action is required. No special conditions are required; it is repeatable.
- Fixed version: io.github.skylot:jadx-core (Maven) 1.5.0.
Low priority for now. Upgrade to io.github.skylot:jadx-core (Maven) 1.5.0 or later.
Generated automatically from the record's data: CVSS (NVD and CNA), CISA KEV and SSVC, FIRST EPSS, exploit sources, fixed versions. How we calculate it
Primary sources: OSV
### Summary when jadx parses a resource file, there is an escape problem with the style file, which can overwrite other files in the directory when saving the decompile result. Although I don't think this vulnerability realizes path traversal in the true sense of the word , I reported it anyway ### Details I see that getResAlias does something with the filename. ```java private String getResAlias(int resRef, String origKeyName, @Nullable FieldNode constField) { ``` but type style will return the original filename directly. 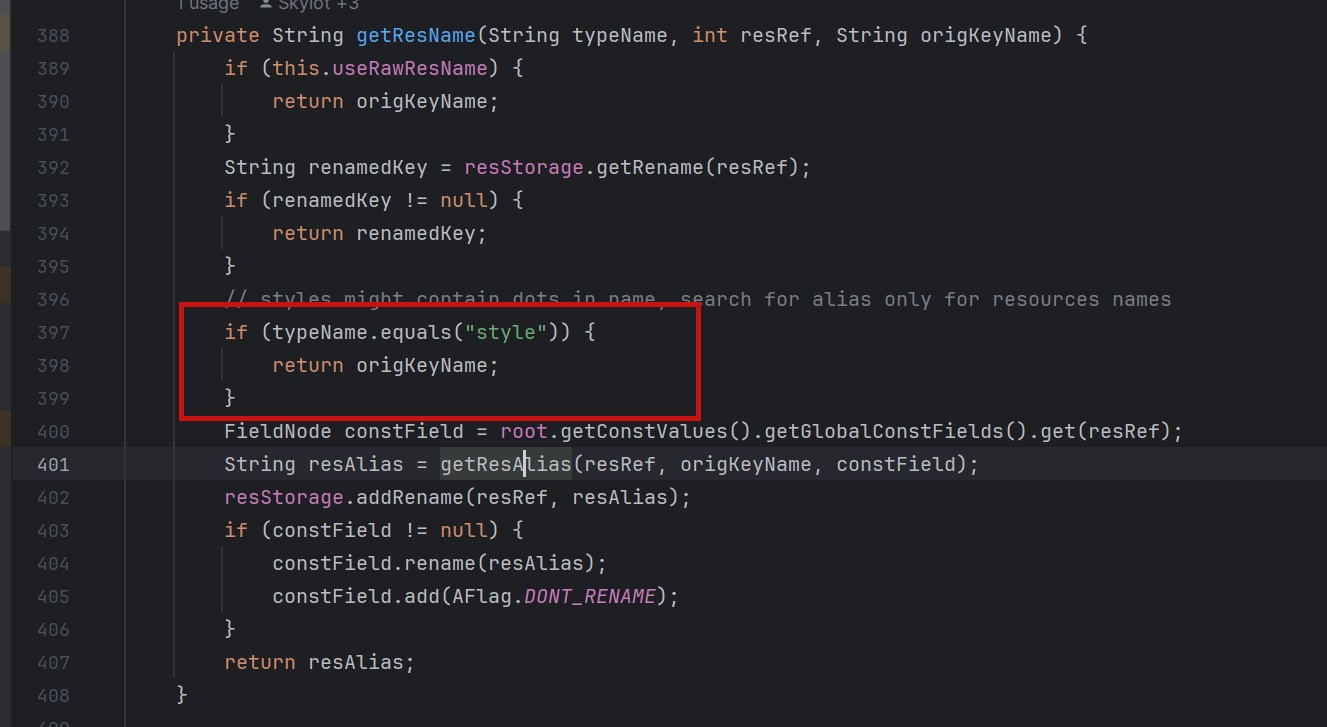 so our goal is to take a malicious file that was originally of type raw, modify its type to style, trick jadx into #### step1 create an android project using androidstudio and create a raw folder with the name attack_file_sayhiiiiiiiiiiiii, it doesn't matter what the content is! 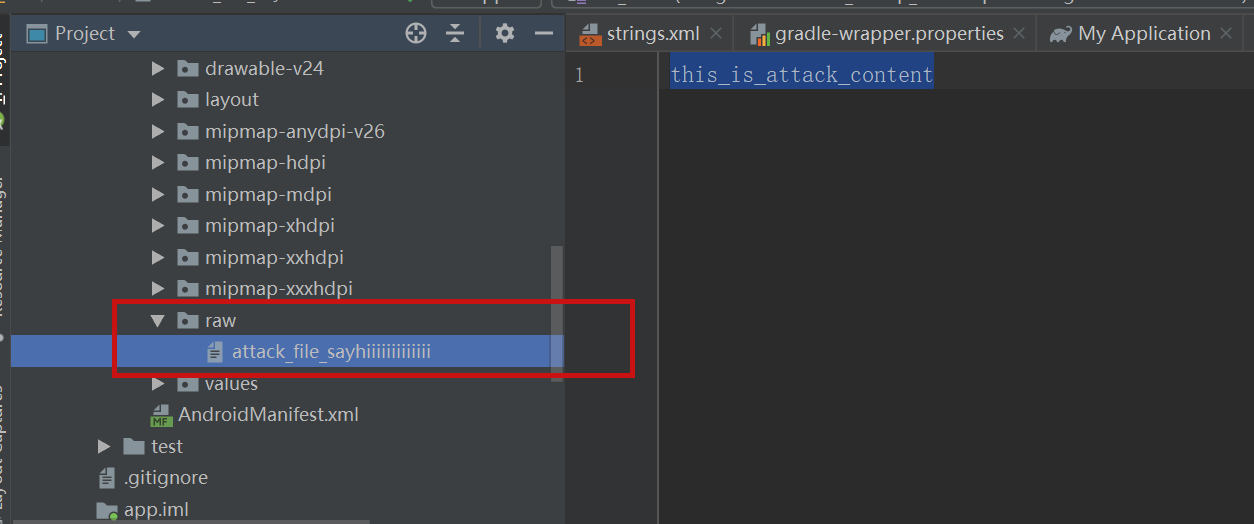 generate an initial APK #### step2 extract this initial APK using ZIP software to get resources.arsc 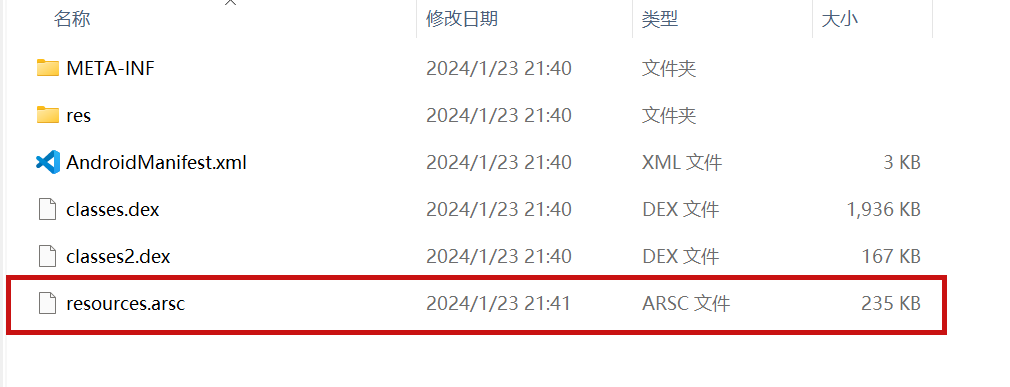 drop resources.arsc into 010editor #### step3 search for the previous filename attack_file_sayhiiiiiiiiiiiii , two will appear here, we choose the second one 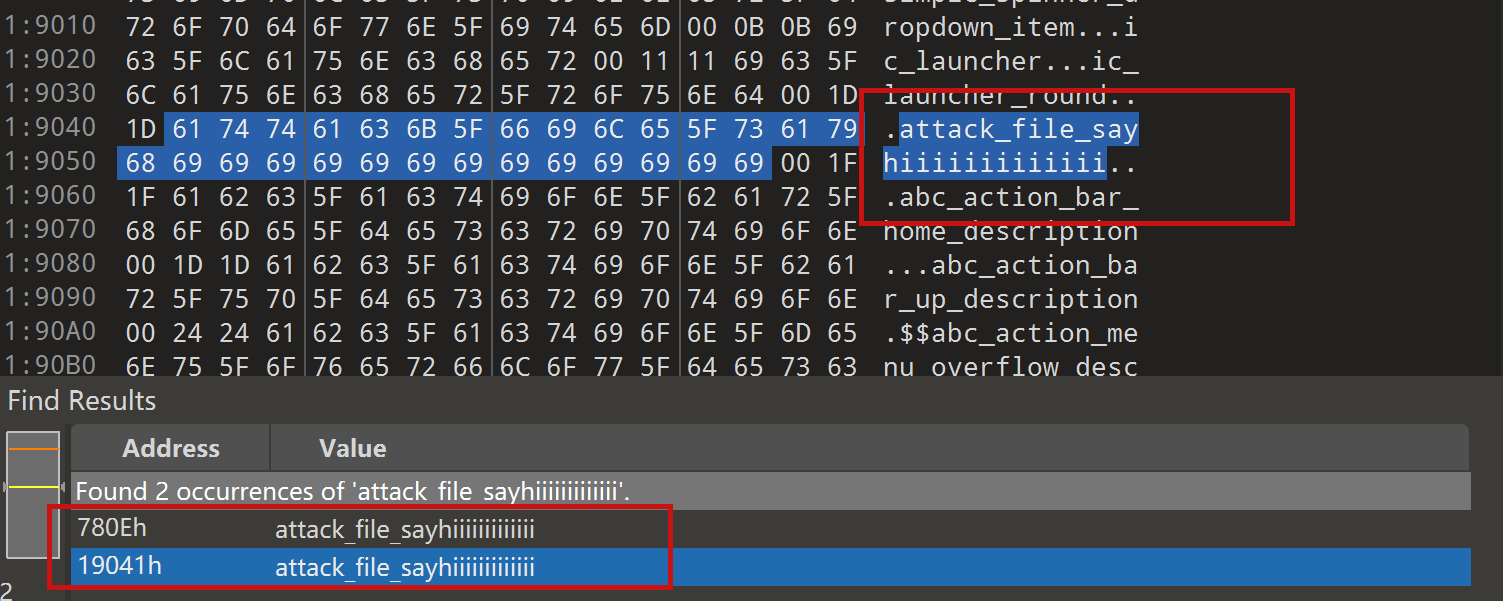 let's change the name of the file here. I'll change it to ../../_file_sayhiiiiiiiiiiiii note that you can only overwrite files in the folder where the decompile was saved. 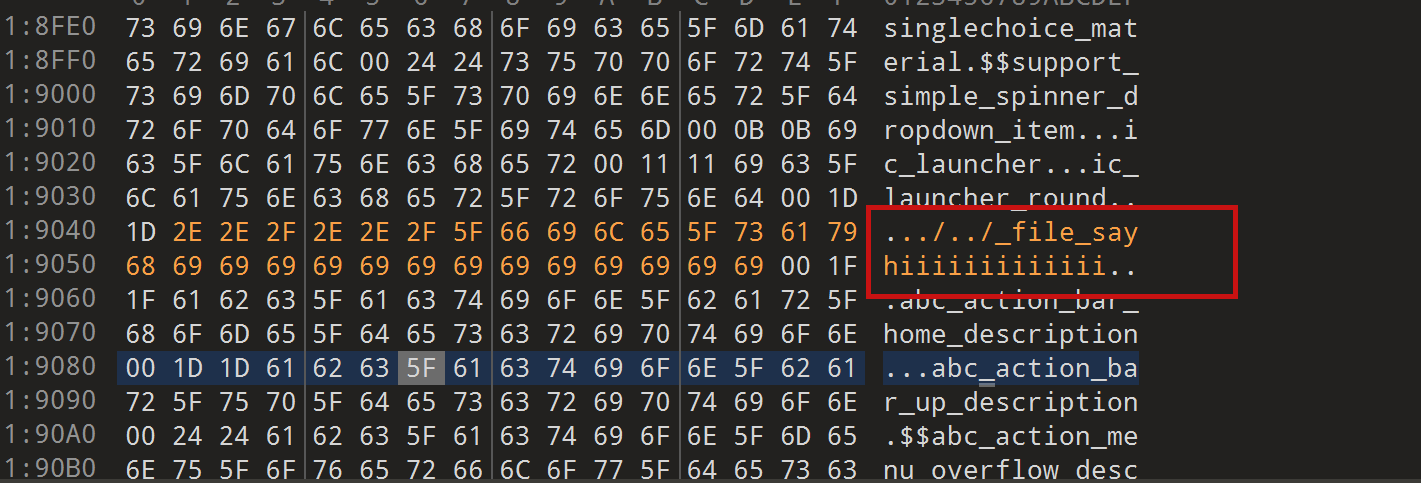 #### step4 change the type of this file to style 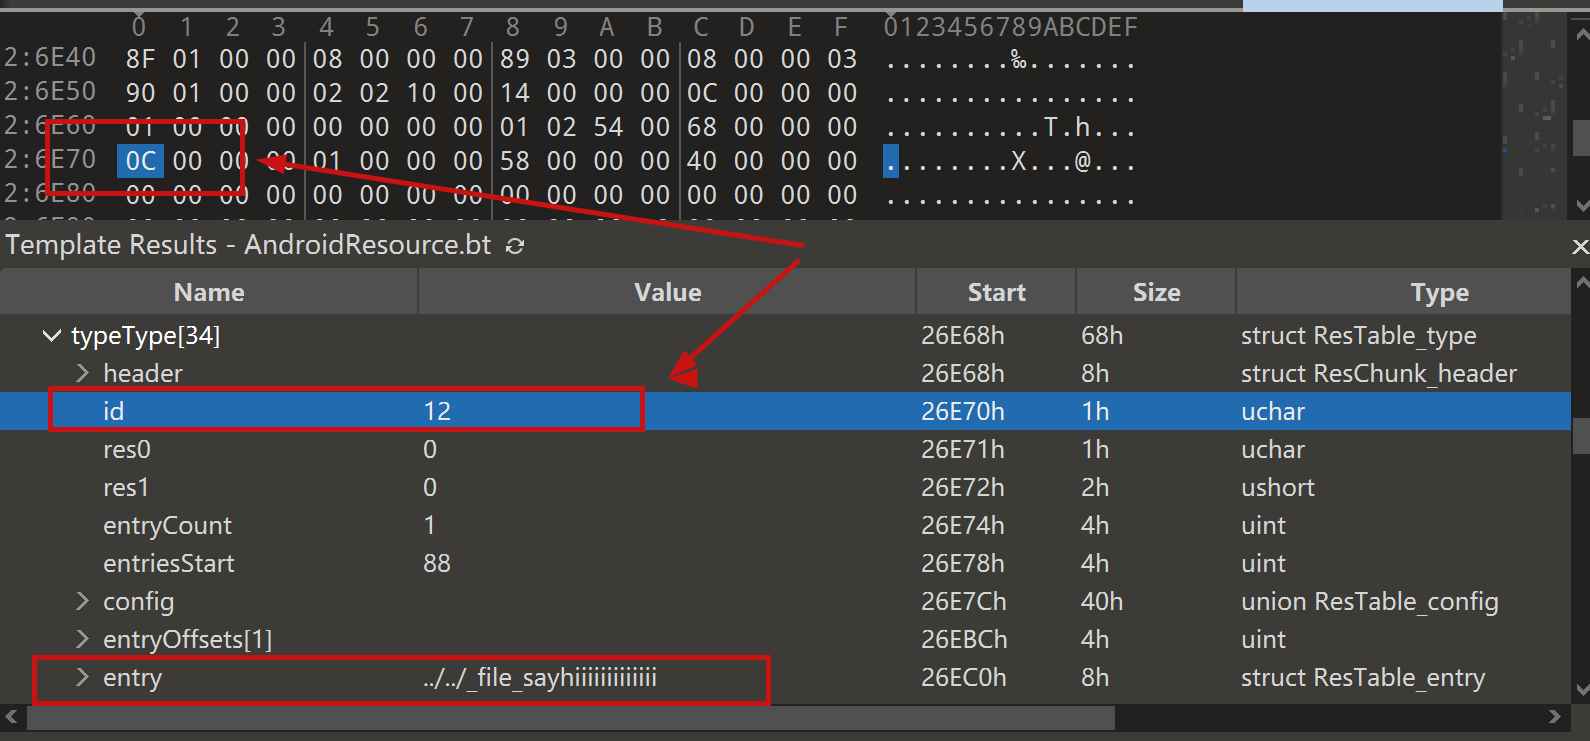 modified to 0E 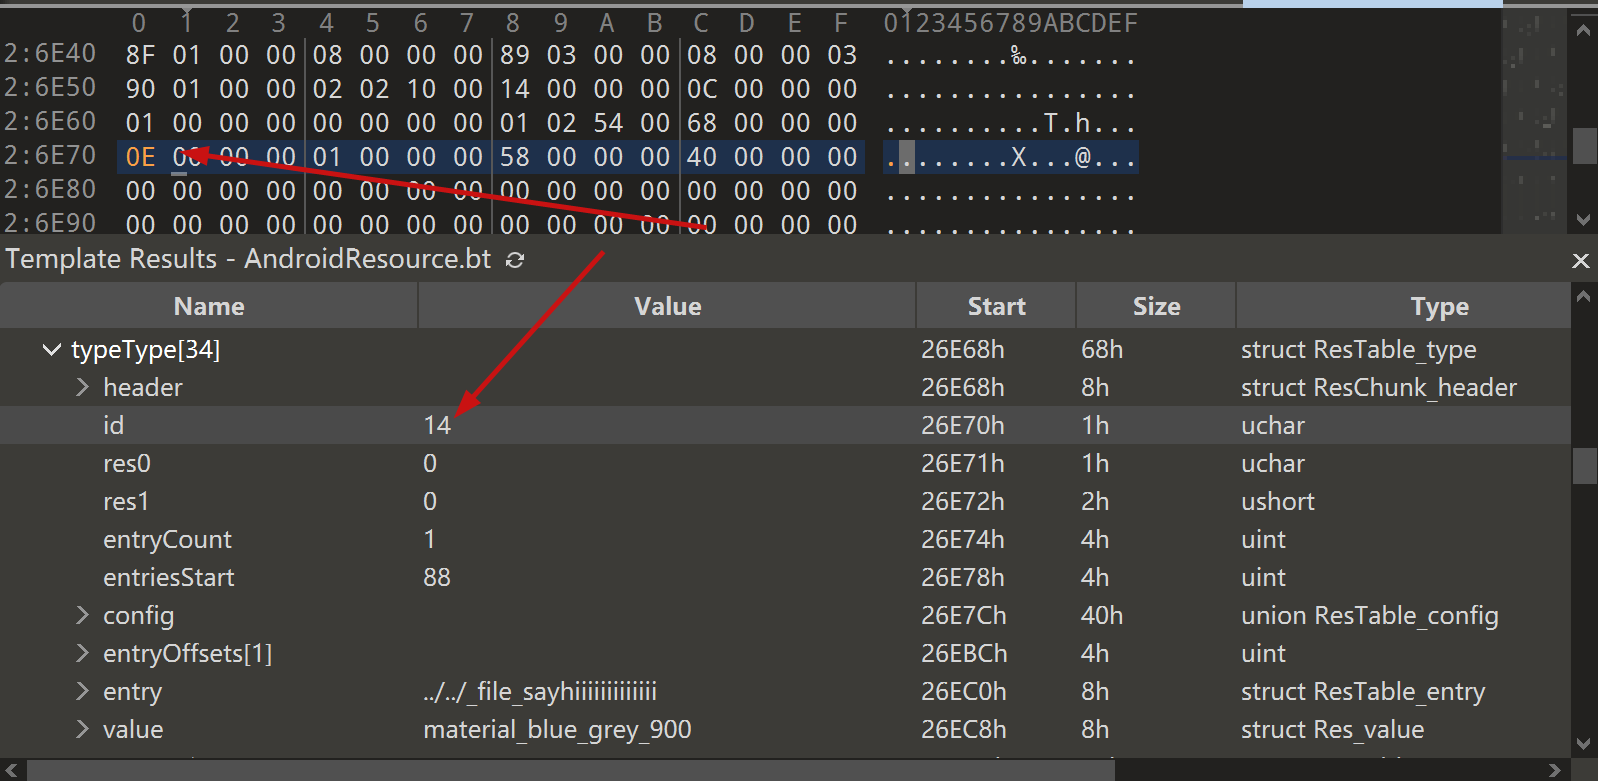 #### step5 After saving, re-compress the whole folder into a zip, then change the extension to APK. open it with JADX and you can see that it has been changed to a style type. 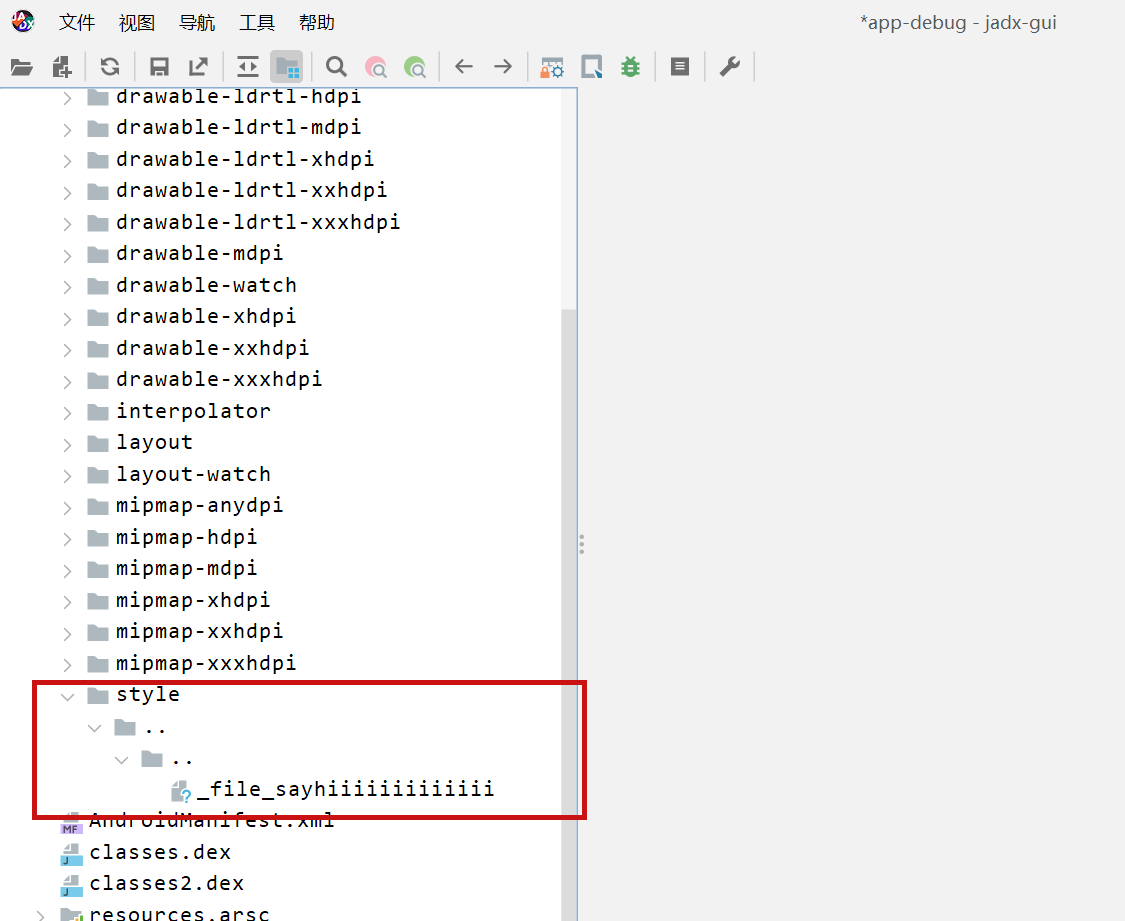 click save all 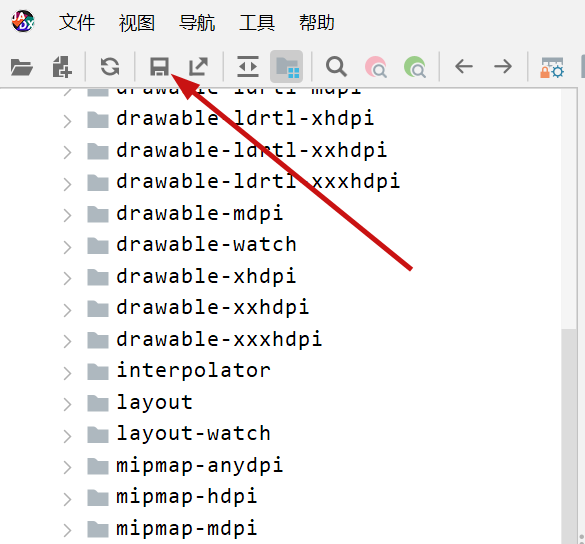 you can see the file escaping. 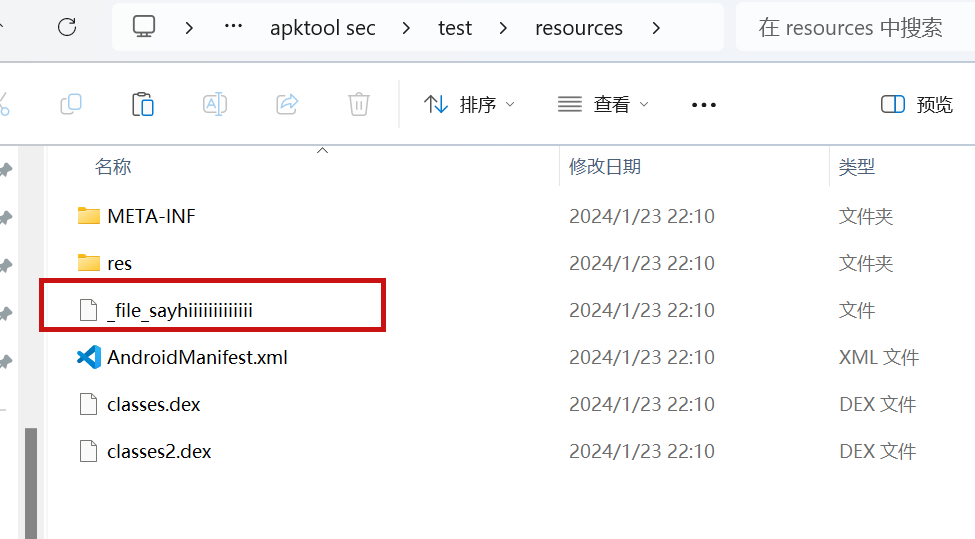 so we can also construct a 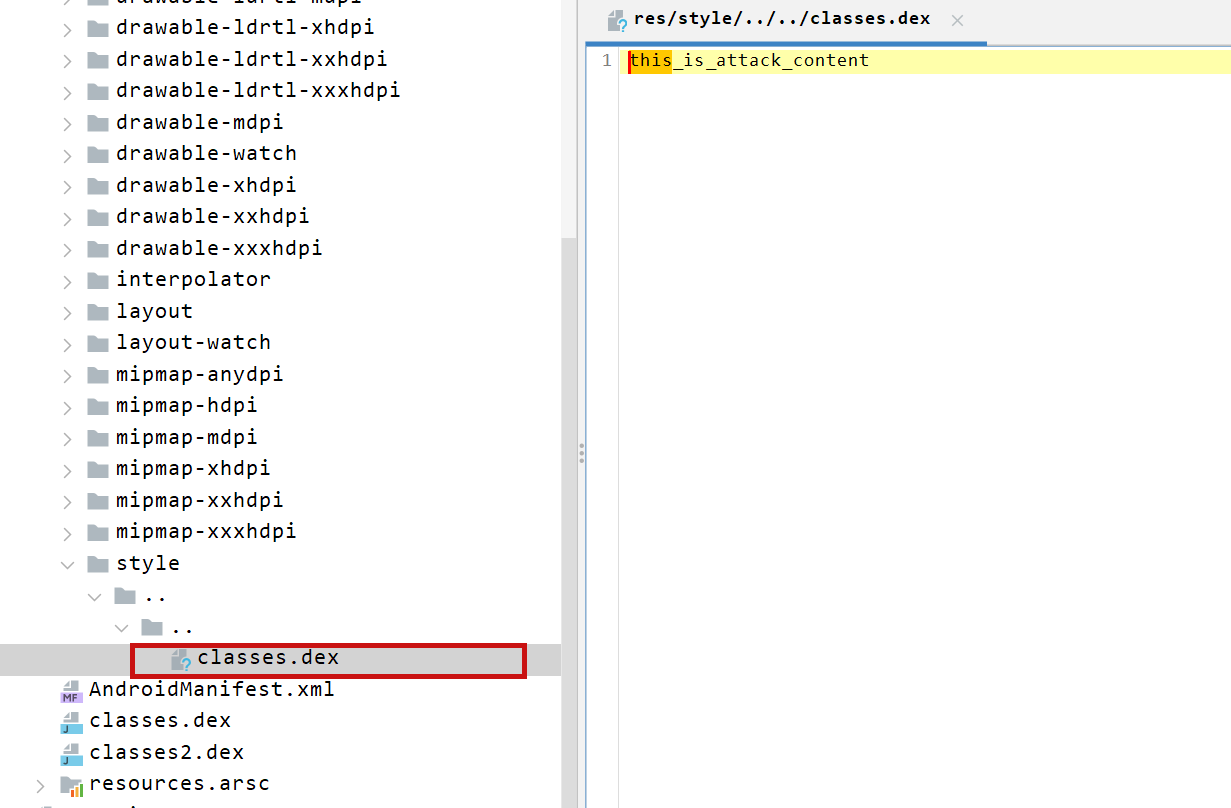 so the classes.dex file is also replaced here 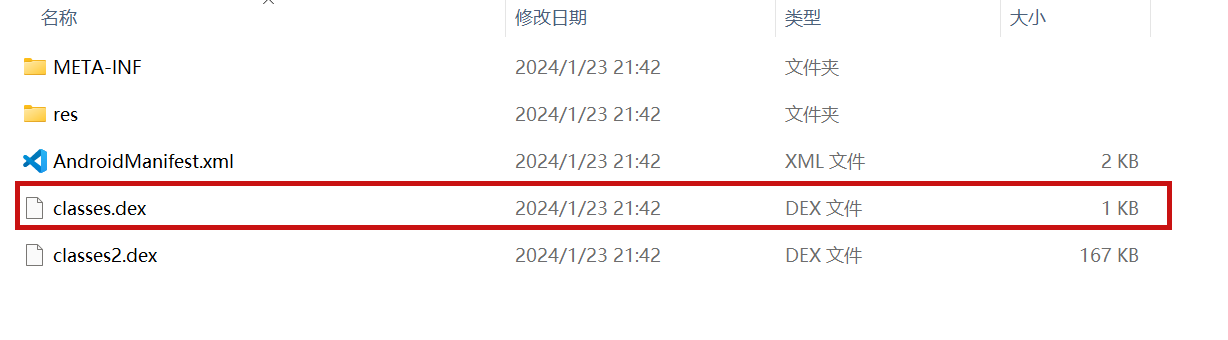 ### PoC the details above have been written ### Impact latest version
- Published
- Apr 22, 2024
- Updated
- Dec 5, 2024
- EPSS
- —
- CWE
- CWE-22
Report tools
Action score
13
Low priority for now.
- CVSS
- 13 / 40 · 3.3 / 10
- CISA KEV
- 0 / 30 · Not listed
- EPSS
- 0 / 30 · —
Get told when this record changes
- Not in KEV: no record of exploitation in the wild
- No public exploit code on record
- A fix has been released
If any of these changes, we'll tell you in the daily email digest.
Is your version affected? Check itNoroxi analysis
What does it mean in your environment?
The assessment above is generated automatically from the record's data; it doesn't know your environment. Our team verifies on your systems whether this vulnerability is actually exploitable and which mitigation is enough.
We use this product, ask for helpAffected systems
Is your version affected?
Pick the product and type the version you run. It's compared with this record's version ranges in your browser; the version isn't sent anywhere.
| Vendor | Product | CPE |
|---|---|---|
| Maven | io.github.skylot:jadx-core | pkg:maven/io.github.skylot/jadx-core |
Package-level exposure
OSV and GitHub Advisory data: ecosystem, package and range. SBOM matching uses this table.
| Ecosystem | Package | Affected range | Fix |
|---|---|---|---|
| Maven | io.github.skylot:jadx-core | before 1.5.0 | 1.5.0 |
Same product
Maven: all recordsOther highest-scoring records for the same primary product.
- GHSA-fjh6-p566-wr6qskylot jadx affected by Incorrect Behavior Order in vulnerable dependency0Monitor
Remediation
Which version to upgrade to
Fix versions compiled from the vendor, package registries and Microsoft. Verify the vendor's note before upgrading.
| Product / package | Fixed version | Source |
|---|---|---|
| Maven:io.github.skylot:jadx-core | 1.5.0 | Package registry (OSV) |
Exploit status
No known public exploit
No public exploit has been observed yet. That doesn't mean you're safe, only that the bar is a little higher.
Research context
For pentesters and researchers: attack profile, score disagreement, timeline, patch commits, credits, variant and chain candidates, bug bounty scope. All derived from existing data; no exploit code.
Timeline
From publication to today: proof of concept, Metasploit module, CISA KEV and fix record. Dates are as reported by the sources.
No dated events beyond publication.
Patch and commit links
Commit, PR and diff links among the references. A starting point for patch-diffing and variant hunting; fixes, not exploits.
Not on record for this CVE: EPSS history · researcher credit · variant or chain candidate · public bounty program.
Technical details
Attack conditions
- Someone with local access to the system can trigger it.
- A low-privileged account is enough.
- No user action is required.
- No special conditions are required; it is repeatable.
If successful
- Confidentiality
- none
- Integrity
- low · data or configuration can be modified
- Availability
- none
- Attack vector
- Local
- Attack complexity
- Low
- Privileges required
- Low
- User interaction
- None
- Scope
- Unchanged
- Confidentiality impact
- None
- Integrity impact
- Low
- Availability impact
- None
Weakness class (CWE)
CWE-22 · Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')CVSS vector
CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N
osv
Root cause
A user-supplied file name is joined with the allowed directory, but the result is never checked to confirm it is still inside that directory.
The bug in code
The whole CWE-22 classA representative example of this vulnerability class. Not the vendor's source code; it shows the faulty pattern and its fix.
Vulnerable
const file = path.join(ROOT, req.query.name);
res.sendFile(file);Fixed
const file = path.resolve(ROOT, req.query.name);
if (!file.startsWith(ROOT + path.sep)) {
return res.sendStatus(400);
}
res.sendFile(file);Attack context
MITRE CAPEC attack patterns and ATT&CK techniques for this weakness class (CWE). A starting point for detection rules and threat hunting.
Attack patterns (CAPEC)
- Path TraversalCAPEC-126likelihood: High · Very High
- Using Slashes and URL Encoding Combined to Bypass Validation LogicCAPEC-64likelihood: High · High
- Manipulating Web Input to File System CallsCAPEC-76likelihood: High · Very High
- Using Escaped Slashes in Alternate EncodingCAPEC-78likelihood: High · High
- Using Slashes in Alternate EncodingCAPEC-79likelihood: High · High
ATT&CK techniques
—
Change log (1)
- Fix✗ → ✓
For records you follow, these changes also arrive as notifications. →
References
Show all references (2 more)Show less
Vendor advisories and official records. Exploit/PoC links are deliberately left out.